Duplicates and copies of security issues
TRON.ASOC uses mechanisms to detect copies and deduplicate security issues. They help find duplicate records and reduce redundant information in the results.
Difference between a copy and a duplicate
A copy is a vulnerability that exactly matches a previously recorded vulnerability detected by the same scanning tool.
A duplicate is a similar vulnerability that may come from another tool or may have changed as a result of a code change. Duplicates aren't copies.
Detecting copies based on a hash
The system detects copies of vulnerabilities based on a hash. The hash is generated from the following vulnerability fields:
Tool_Type_name—scanning tool type;CVE—CVE identifier;CWE—CWE identifier;Source_file—source file path;Lib_name—library name;Lib_version—library version;Category—vulnerability category;Source_object—source object;Line—line number;Matched_Code—matching code fragment.
The system detects copies as follows:
- When you start TRON.ASOC with hashing enabled, the system recalculates the hash for all existing vulnerabilities.
- The system detects and deletes copies, keeping the earliest record from each group of copies.
- The system determines the status of the remaining vulnerability according to the following rule:
New—if at least one vulnerability among the copies had an open status;Fixed—if none of the copies had an open status.
You can change hash parameters only through the configuration file. You can't manage them through the user interface.
The number of vulnerabilities in the scan results reflects hashing.
Issue deduplication
Deduplication automatically finds and combines duplicate security issue records.
For more information about configuring global Deduplication rules, see the corresponding section.
Finding duplicate security issues
To view duplicate security issues, follow these steps:
- Go to the Issues section.
- Open the security issue to which deduplication may apply.
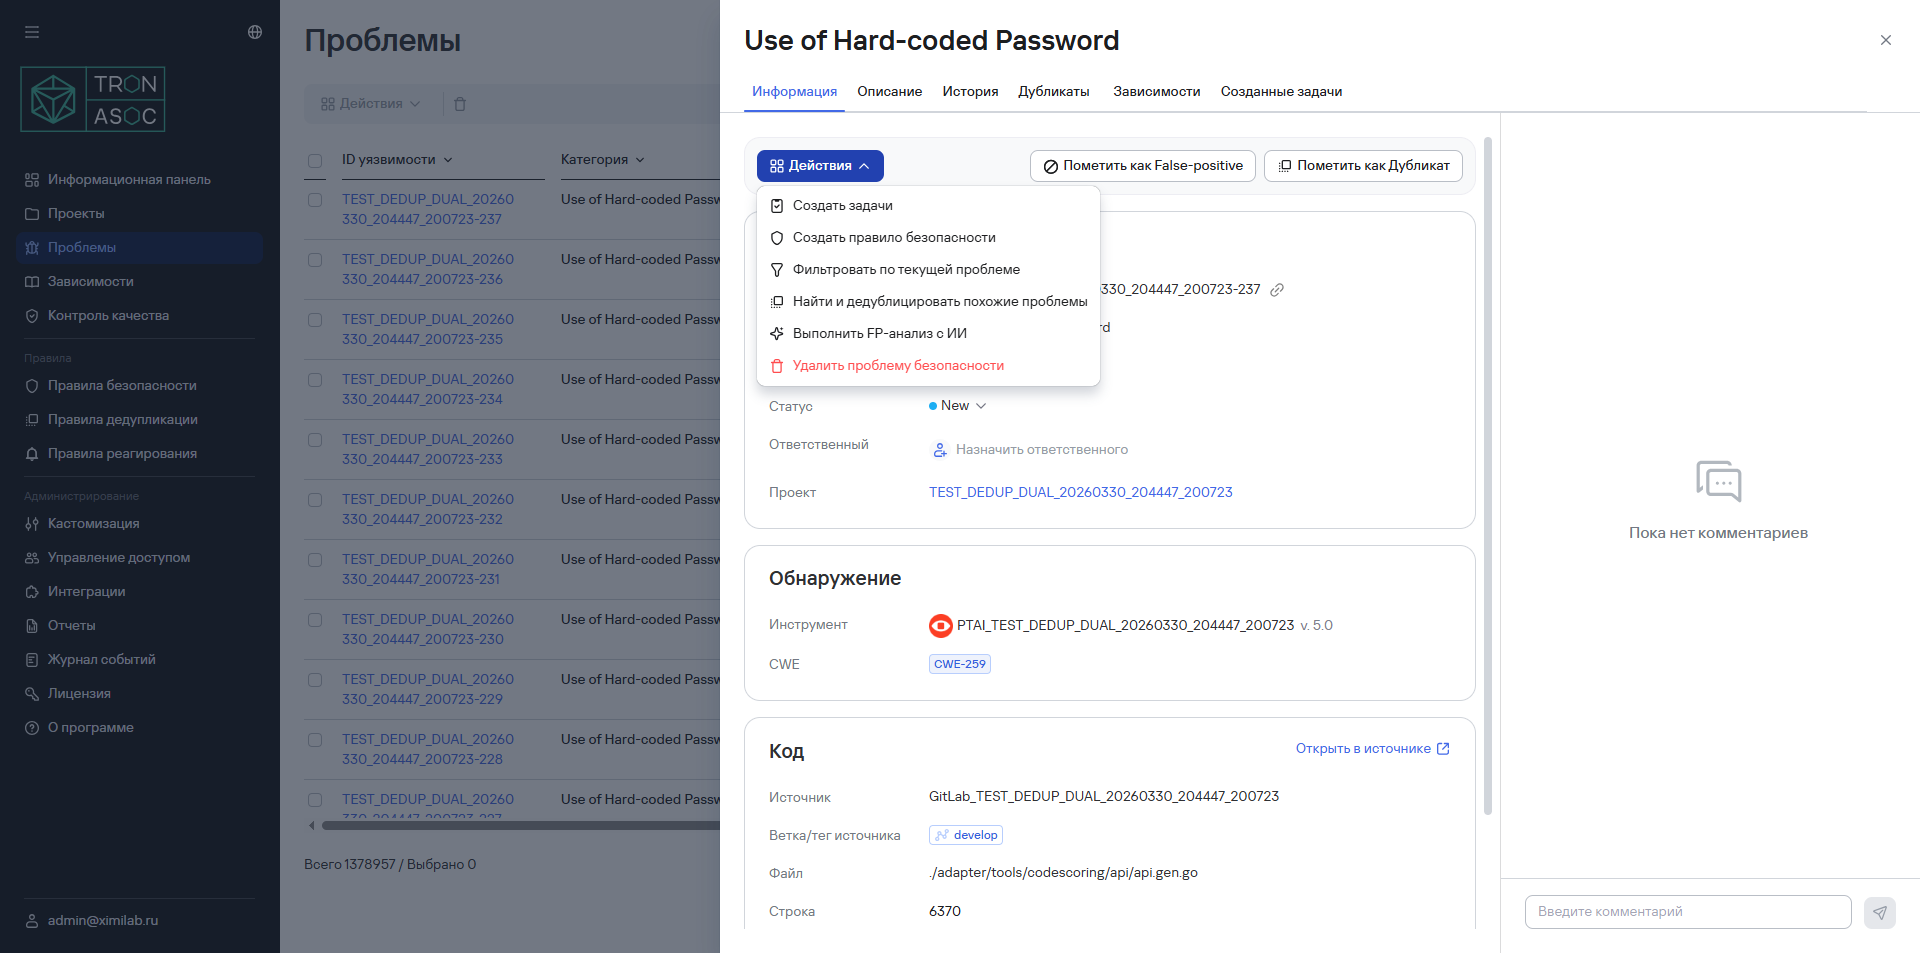
- Select Find and deduplicate similar issues from the Actions drop-down list.
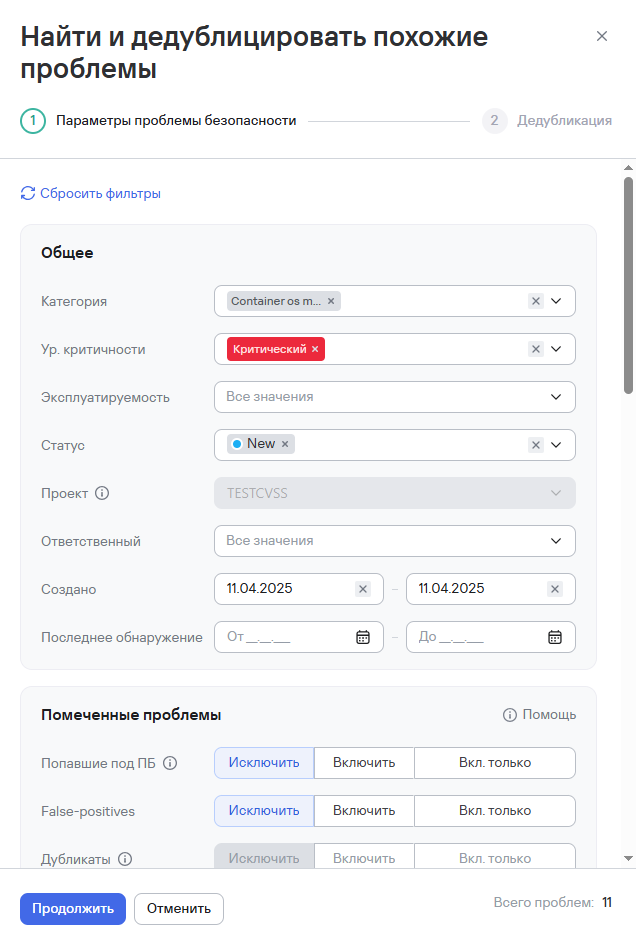
- Set the required filters in the window that opens on the right.
-
Select Continue.
-
Select the vulnerabilities from the list in the new window on the right.
-
Select Mark as duplicate.
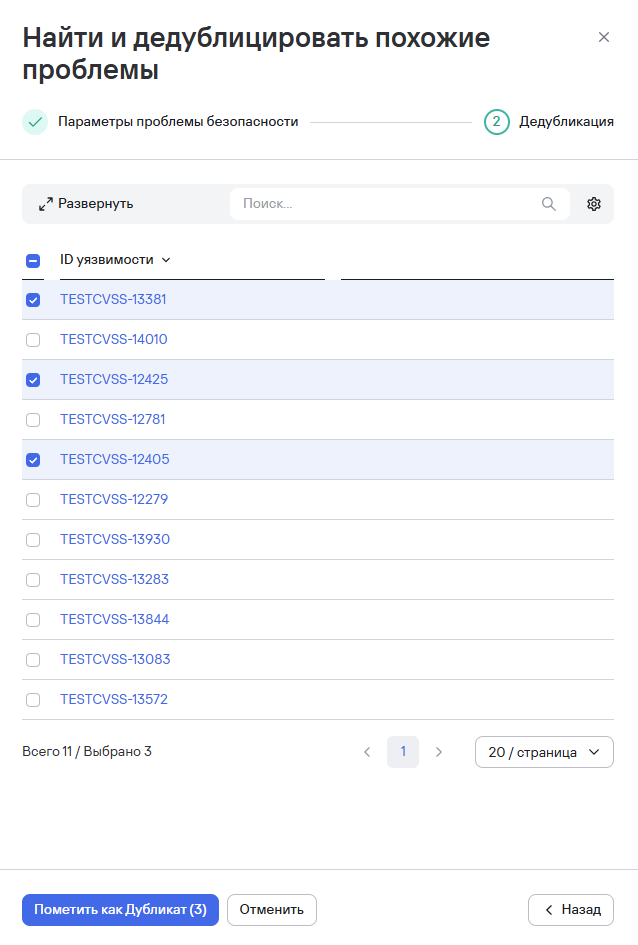
After you complete these steps, the system marks the issues as duplicates and links them to the new issue. The system interface also displays a notification.