Security issue duplicates and copies
TRON.ASOC uses mechanisms to detect copies and deduplicate security issues. These mechanisms help find duplicate records and reduce redundant information in the results.
Difference between a copy and a duplicate
A copy is a vulnerability whose hash completely matches the hash of an existing vulnerability. The subsection Hash-based copy detection describes the fields included in the hash. Because you can configure the fields included in the hash through a configuration file, a matching hash doesn't necessarily mean that both vulnerabilities were detected by the same scanning tool. If the Tool_Type_name field is excluded from the hash, the system can identify a vulnerability found by another tool as a copy.
When hashes match, the system doesn't create a new record. It doesn't save the copy. Instead, it updates the last detected date for the existing vulnerability. For example, if you upload the same report with the same vulnerability 50 times, the system saves the vulnerability during the first upload. During each of the next 49 uploads, it only updates the last detected date and doesn't create additional records.
A duplicate is a vulnerability whose hash differs from the hash of another vulnerability by at least one field but is grouped with that vulnerability according to deduplication rules or manually marked as a duplicate by a user. A duplicate isn't associated with a scanning tool. For example, the same tool can find two duplicate vulnerabilities. Duplicates aren't copies.
Hash-based copy detection
The system uses a hash-based mechanism to detect vulnerability copies. The hash consists of the following vulnerability fields:
Tool_Type_name—scanning tool type;CVE—CVE identifier;CWE—CWE identifier;Source_file—source file path;Lib_name—library name;Lib_version—library version;Category—vulnerability category;Source_object—source object;Line—line number;Matched_Code—matching code fragment.
Because you can configure these fields through a configuration file, you can, for example, exclude Tool_Type_name. The system then identifies matching vulnerabilities as copies regardless of which tool detected them.
The system detects copies as follows:
- When you start TRON.ASOC with hashing enabled, the system recalculates the hash for all existing vulnerabilities.
- The system detects and deletes copies, keeping the earliest record from each set of copies.
- The system determines the remaining vulnerability's status according to the following rule:
New—if at least one of the copies had an open status;Fixed—if none of the copies had an open status.
The system applies the same logic during each new report upload. If the hash of a newly detected vulnerability matches the hash of an existing vulnerability, the system only updates the last detected date for the existing vulnerability. It doesn't create a new vulnerability record.
You can change hash parameters only through the configuration file. You can't manage them through the user interface.
The system displays the number of vulnerabilities in the scan results with hashing applied.
Issue deduplication
Deduplication automatically finds and combines duplicate security issue records.
For more information about configuring global Deduplication rules, see Deduplication rules.
Finding security issue duplicates
To view security issue duplicates, follow these steps:
- Go to the Issues section.
- Open the security issue that deduplication might apply to.
- Select Find and deduplicate similar issues from the Actions dropdown list.
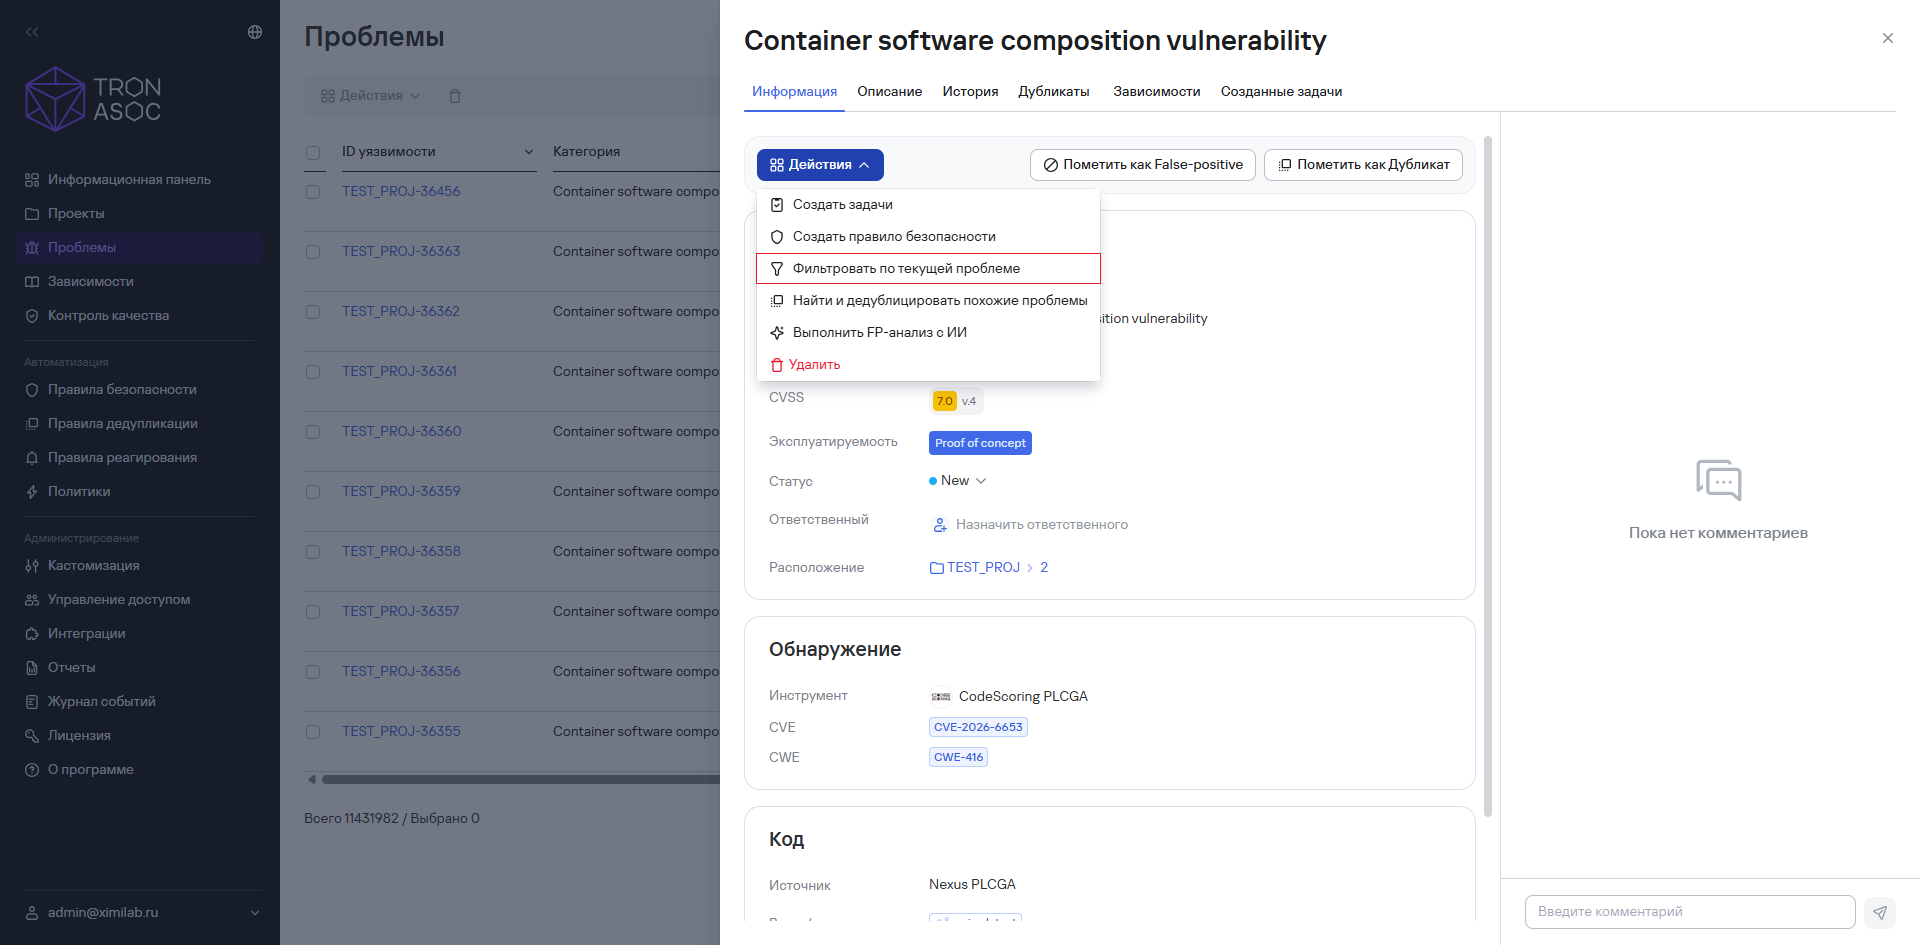
- In the window that opens on the right, set the required filters.
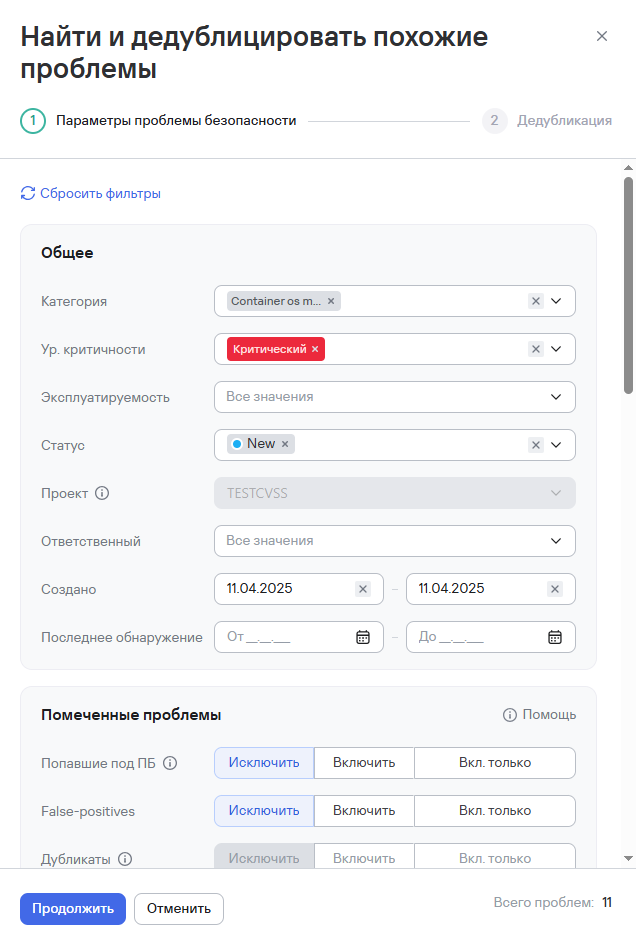
-
Select Continue.
-
Select vulnerabilities from the list in the new window on the right.
-
Select Mark as duplicate.
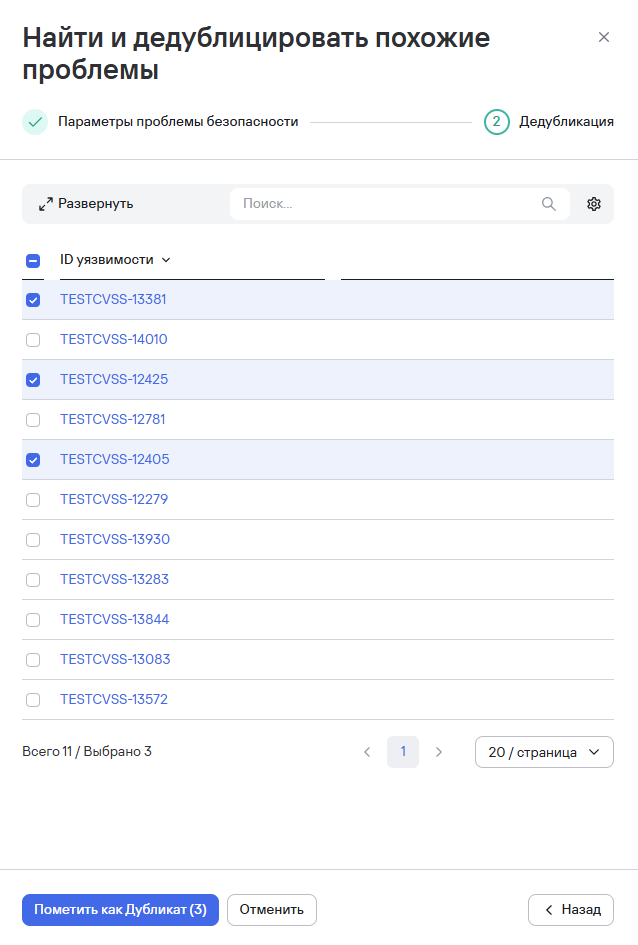
After you complete these steps, the system marks the issues as duplicates and links them to the new issue. The system interface also displays a notification about this.