Actions for scan sources
This section describes how to add, edit, and delete scan sources, the supported scan sources, and combinations of scan sources and security tools.
Supported scan sources
The system supports the following scan sources:
- App URL;
- Bitbucket;
- GitHub;
- GitLab;
- Harbor;
- Jfrog;
- Nexus;
- Other GIT Repository.
After you upgrade TRON.ASOC to a new version, you must reconfigure integrations with Git Repository sources that don't have a source control system type configured.
Connect an integration with a scan source
To connect integrations with scan sources, users must have at least the following permissions:
- View sources;
- Manage sources;
To connect an integration with a scan source, follow these steps:
- Go to Integrations → Scan sources.
- Select Add scan source.
- Select the type of scan source to connect.
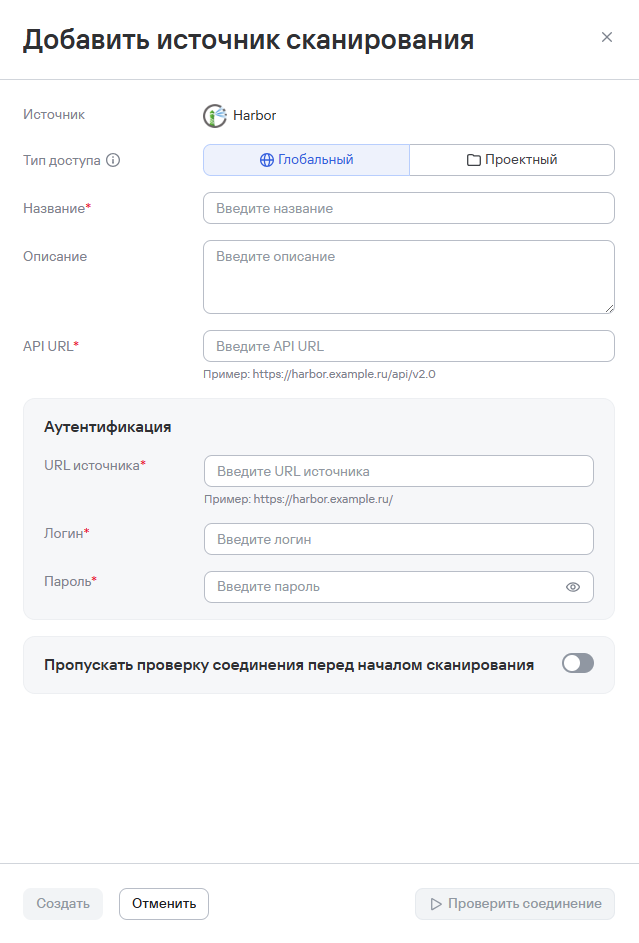
- In the window that opens, specify the following parameters:
-
access type for the scan source:
- Global—the scan source will be available in all projects;
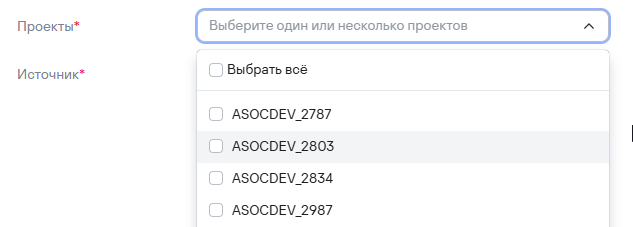
- Project—the scan source will be available only in the selected projects. After selecting this access type, select one or more projects where the scan source will be available.
tipWhen you select the Project access type, select the projects where the integration will be available using the checkboxes.
-
source name;
-
source description;
-
source URL;
-
source API URL. This parameter is available when you select the Harbor, Jfrog, or Nexus source type;
-
method for specifying the repository path—repository path, subdomain, or port. This parameter is available when you select the Jfrog source type;
-
registry URL. This parameter is available when you select the Jfrog or Nexus source type**/
-
- Enter the authentication data for the scan source (API token, username/password).
- If necessary, turn on the option to skip the connection check before Scans start.
- Select Create.
Edit an integration with a scan source
To edit an integration with a scan source, follow these steps:
- Go to Integrations → Scan sources.
- Select the more actions button (
 ) in the row for the required source.
- Select Edit.
- Change the required data.
- Select Save.
Delete an integration with a scan source
To delete one integration with a scan source, follow these steps:
- Go to Integrations → Scan sources.
- Select the more actions button () in the row for the required source.
- Select Delete.
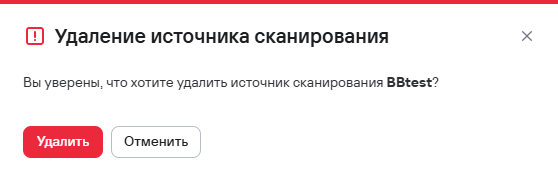
- Confirm the source deletion in the window that opens.
To delete multiple integrations with scan sources, follow these steps:
- Select the scan sources using the checkboxes (
 )
- Select the delete button (
 ) above the source table.
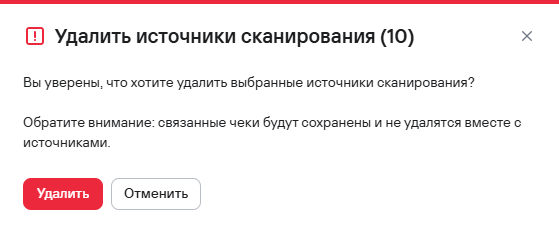
- Confirm the source deletion in the window that opens.
Connect an integration with a scan source of the "Git Repository" type
You can connect one or more Git repositories, as well as all repositories within one namespace, as a scan source.
The following source control system types are available for a Git Repository source:
- GitHub;
- GitLab;
- BitBucket (cloud and server);
- Other GIT Repository.
When you start Scans using a BitBucket source, you can adjust the specified port (for example: ssh://git@bitbucket.int.tronasoc.ru:0000/test/command.git → https://bitbucket.int.tronasoc.ru:0000/test/command.git).
When you connect repositories as scan sources, note the following:
- when you connect a namespace, all repositories in it will be added as a source group and synchronized;
- when you connect multiple repositories, the selected repositories will be added as separate sources and won't be grouped together.
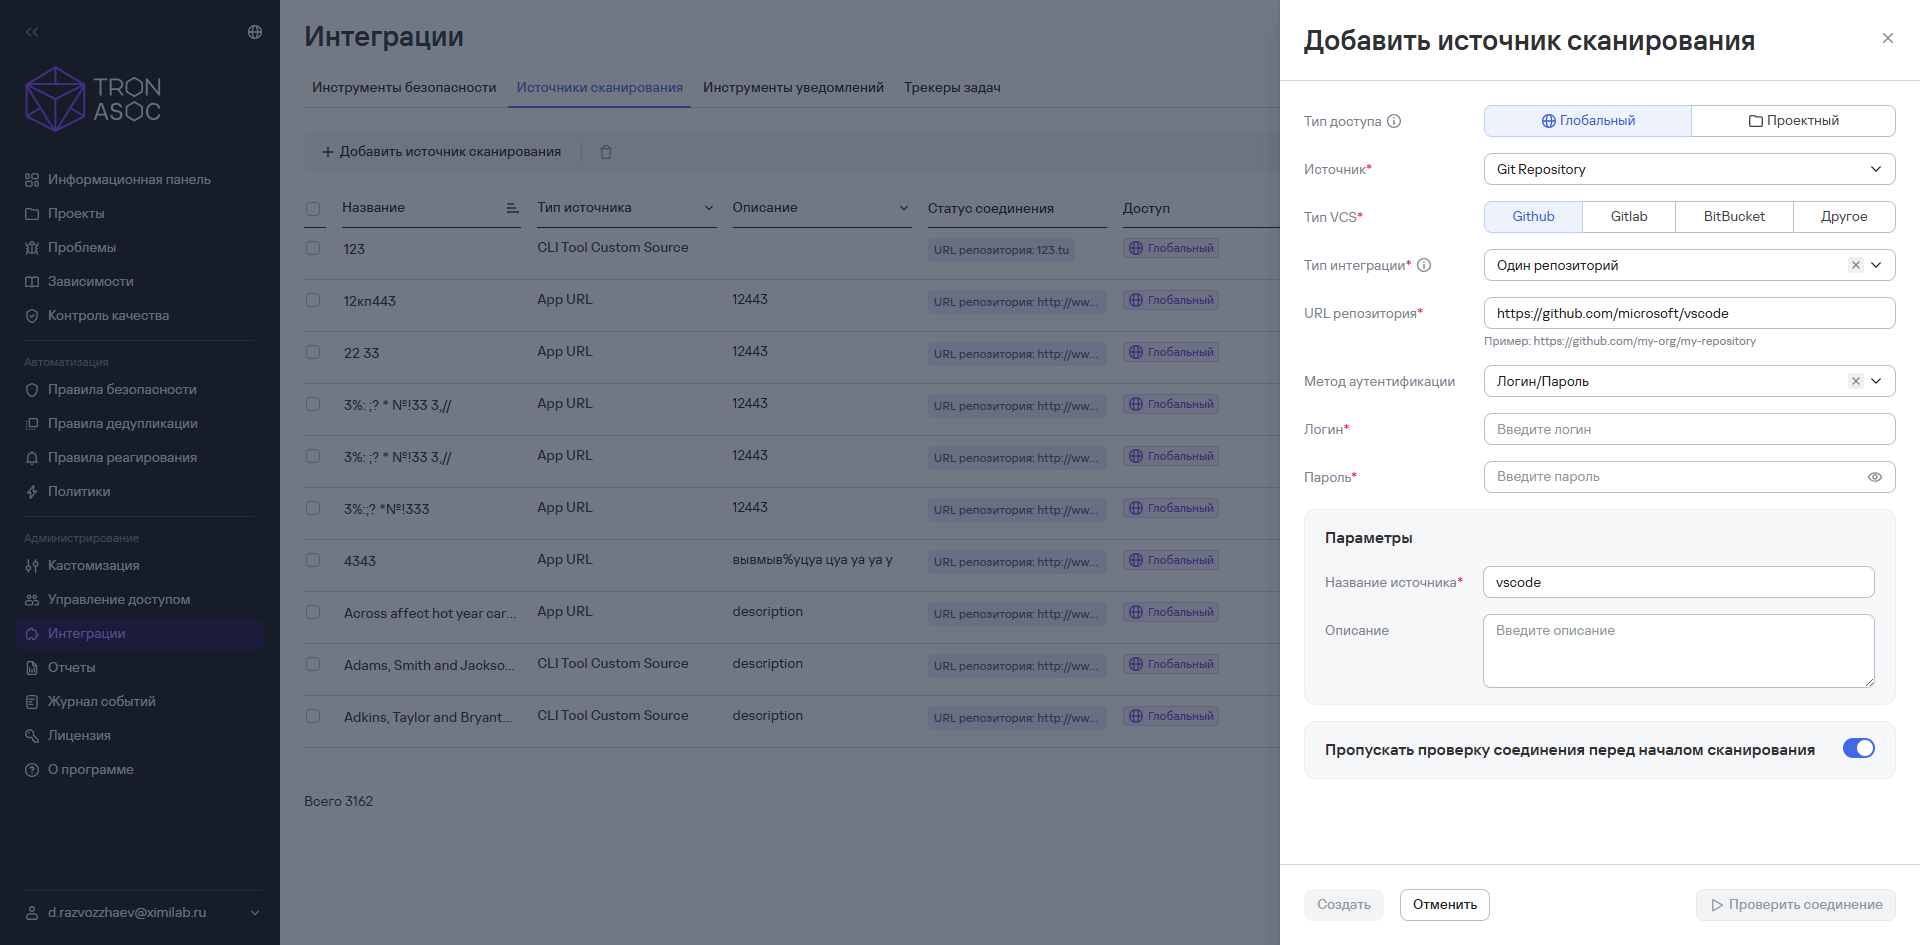
Connect an integration with one scan source of the "Git Repository" type
To connect an integration with one scan source of the Git Repository type, follow these steps:
- Go to Integrations → Scan sources.
- Select Add scan source.
- In the window for adding a source, specify the following data:
- access type (global/project);
- source (Git Repository);
- source control system type;
- integration type (one repository);
- repository URL;
- authentication method and data;
- source name and description.
- If necessary, turn on the option to skip the connection check before Scans start.
- Select Create.
Connect an integration with multiple scan sources of the "Git Repository" type
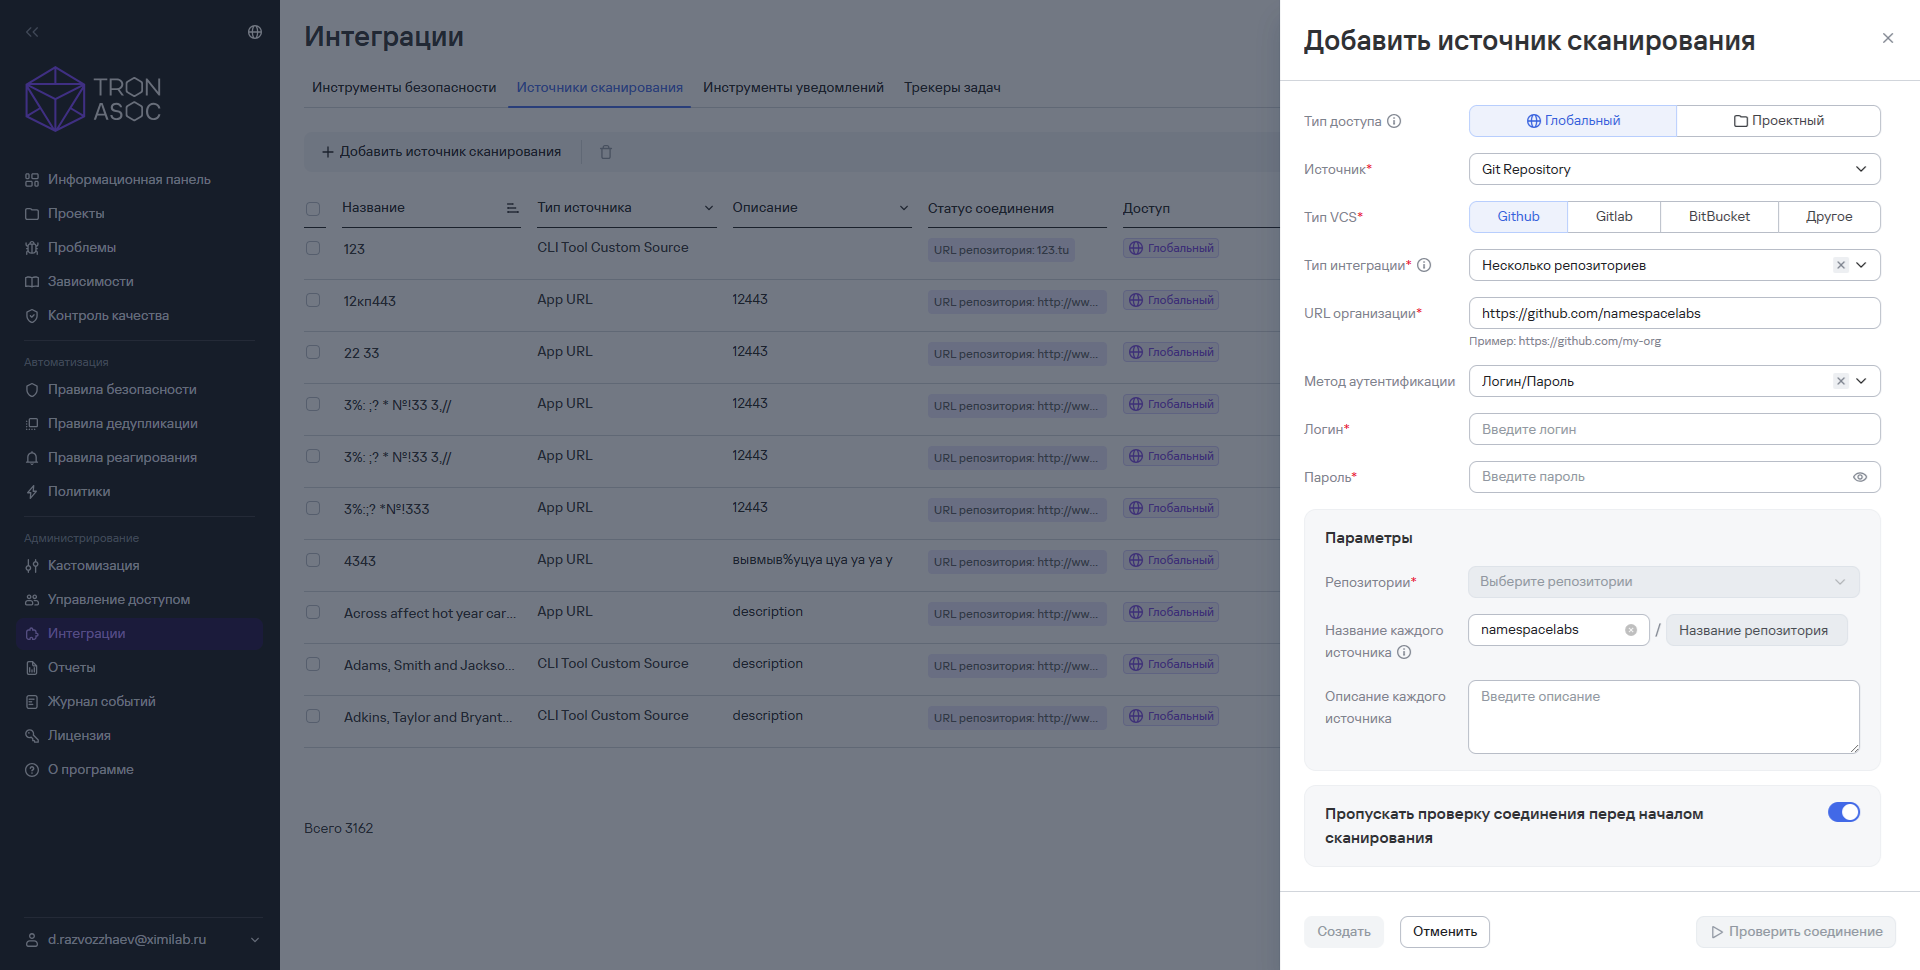
To connect an integration with multiple scan sources of the Git Repository type, follow these steps:
-
Go to Integrations → Scan sources.
-
Select Add scan source.
-
In the window for adding a source, specify the following data:
- access type (global/project);
- source (Git Repository);
- source control system type;
- integration type (multiple repositories);
- organization URL;
- authentication method and data;
-
Specify the parameters:
- repositories;
warningYou can select repositories only if you entered the authentication data for the source correctly.
- name for each source;
infoEach source name consists of the following parts:
- Common prefix (optional).
- Repository name.
- description for each source.
-
If necessary, turn on the option to skip the connection check before Scans start.
-
Select Create.
After you complete all the steps, separate, independent integrations will be created for the selected repositories, and the integration names will match the repository names.
Connect an integration with a namespace containing repositories
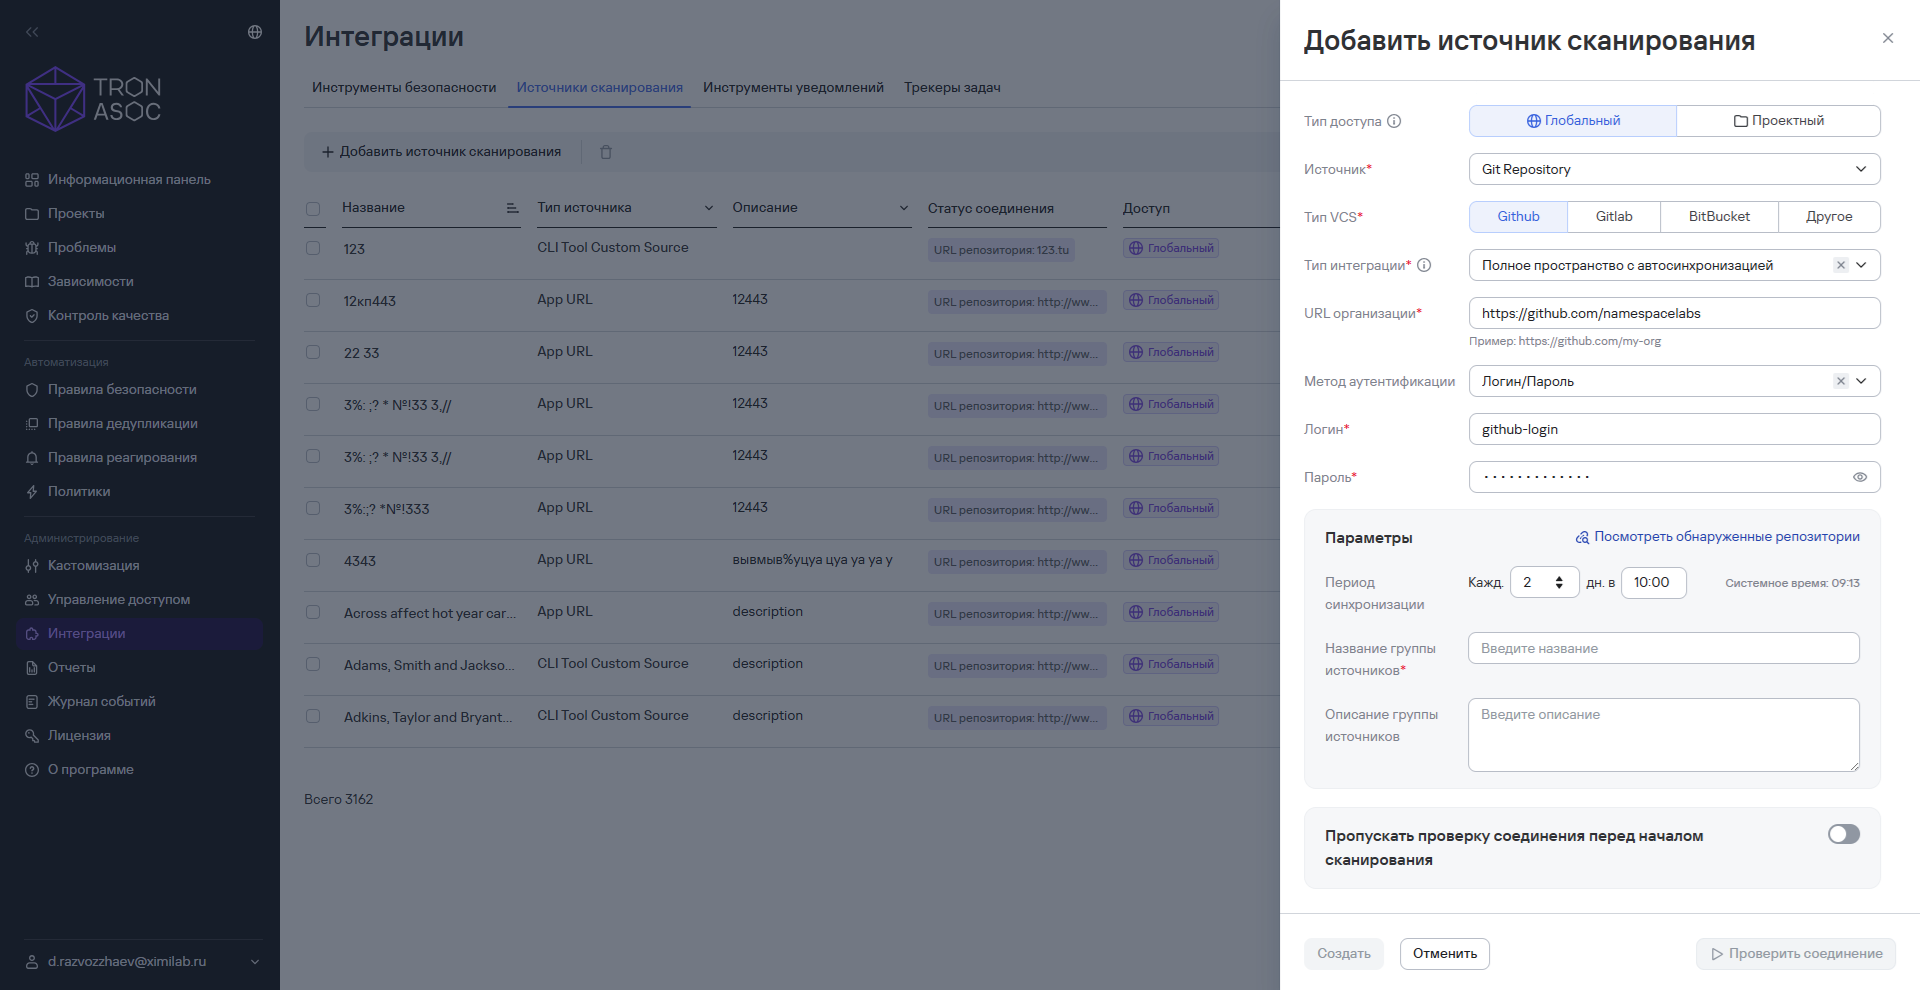
To connect an integration with a namespace containing repositories, follow these steps:
-
Go to Integrations → Scan sources.
-
Select Add scan source.
-
In the window for adding a source, specify the following data:
- access type (global/project);
- source (Git Repository);
- source control system type;
- integration type (entire namespace with automatic synchronization);
- organization URL;
- authentication method and data.
-
Configure the repository synchronization and discovery parameters:
- synchronization period (every N days at HH:MM);
- name and description of the source group.
infoYou can also view repositories automatically discovered in the namespace. To do this, select View discovered repositories.
Automatic repository discovery is possible only if you entered the authentication data for the source correctly.
-
If necessary, turn on the option to skip the connection check before Scans start.
-
Select Create.
After you complete all the steps, the main integration will be created, and all discovered repositories in the namespace will be linked to it as child integrations.
If necessary, configure restricted access to repositories on the source control system side because child integrations in TRON.ASOC are attached to the parent integration and can't be distributed across different projects in TRON.ASOC.
Combinations of scan sources and security tools
The system supports the following combinations of scan sources and security tools:
- CLI tools (ESLint, Gitlab SAST, Trivy, Grype, KICS, Aqua, OWASP Dependency Track, Gitleaks) + CLI Custom source.
- CLI tools that can run in k8s (PVS Studio, Semgrep) + Git Repository. For the current list of CLI tools that can run in k8s, see Run CLI tools in Kubernetes.
- KCS + Nexus/Harbor/Jfrog.
- Appscreener Solar SAST/Solar SCA/PTAI + Git Repository.
- SASTAV + Git Repository.
- CodeScoring + Git Repository/Nexus/Harbor/Jfrog.
- Manual tool + CLI Custom source.
- Appscreener Solar DAST + App URL.
CLI tools from combination 1 can create security checks only with the CLI Custom Source source type.
When you create a check with combination 2, the tool runs in k8s as a job, receives data from the source, performs a security check, and returns a security issue report.
When you create a security check with combinations 3 and 4, you must also specify the source branch/tag. You can specify multiple branches or tags.
When you create a security check with combination 5, you must also specify a set of scan rules and link the source branch/tag to a commit.
When you create a security check with combination 6, you must also specify the security check type (SCA, container SCA, secrets). When you select the secrets type, you must also select a secrets configuration or upload a new one. You must also specify the source branch/tag. You can specify multiple branches or tags.
The Manual tool type can be combined only with the CLI Custom Source source type because tools of this type support only SARIF report uploads.