Access management
In the Access management section, users can:
- add, edit, and archive users;
- reset user passwords;
- add, edit, and delete user roles;
- assign roles to users;
- add, edit, and delete user groups;
- group users;
- configure LDAP authentication settings;
- configure SSO connection settings;
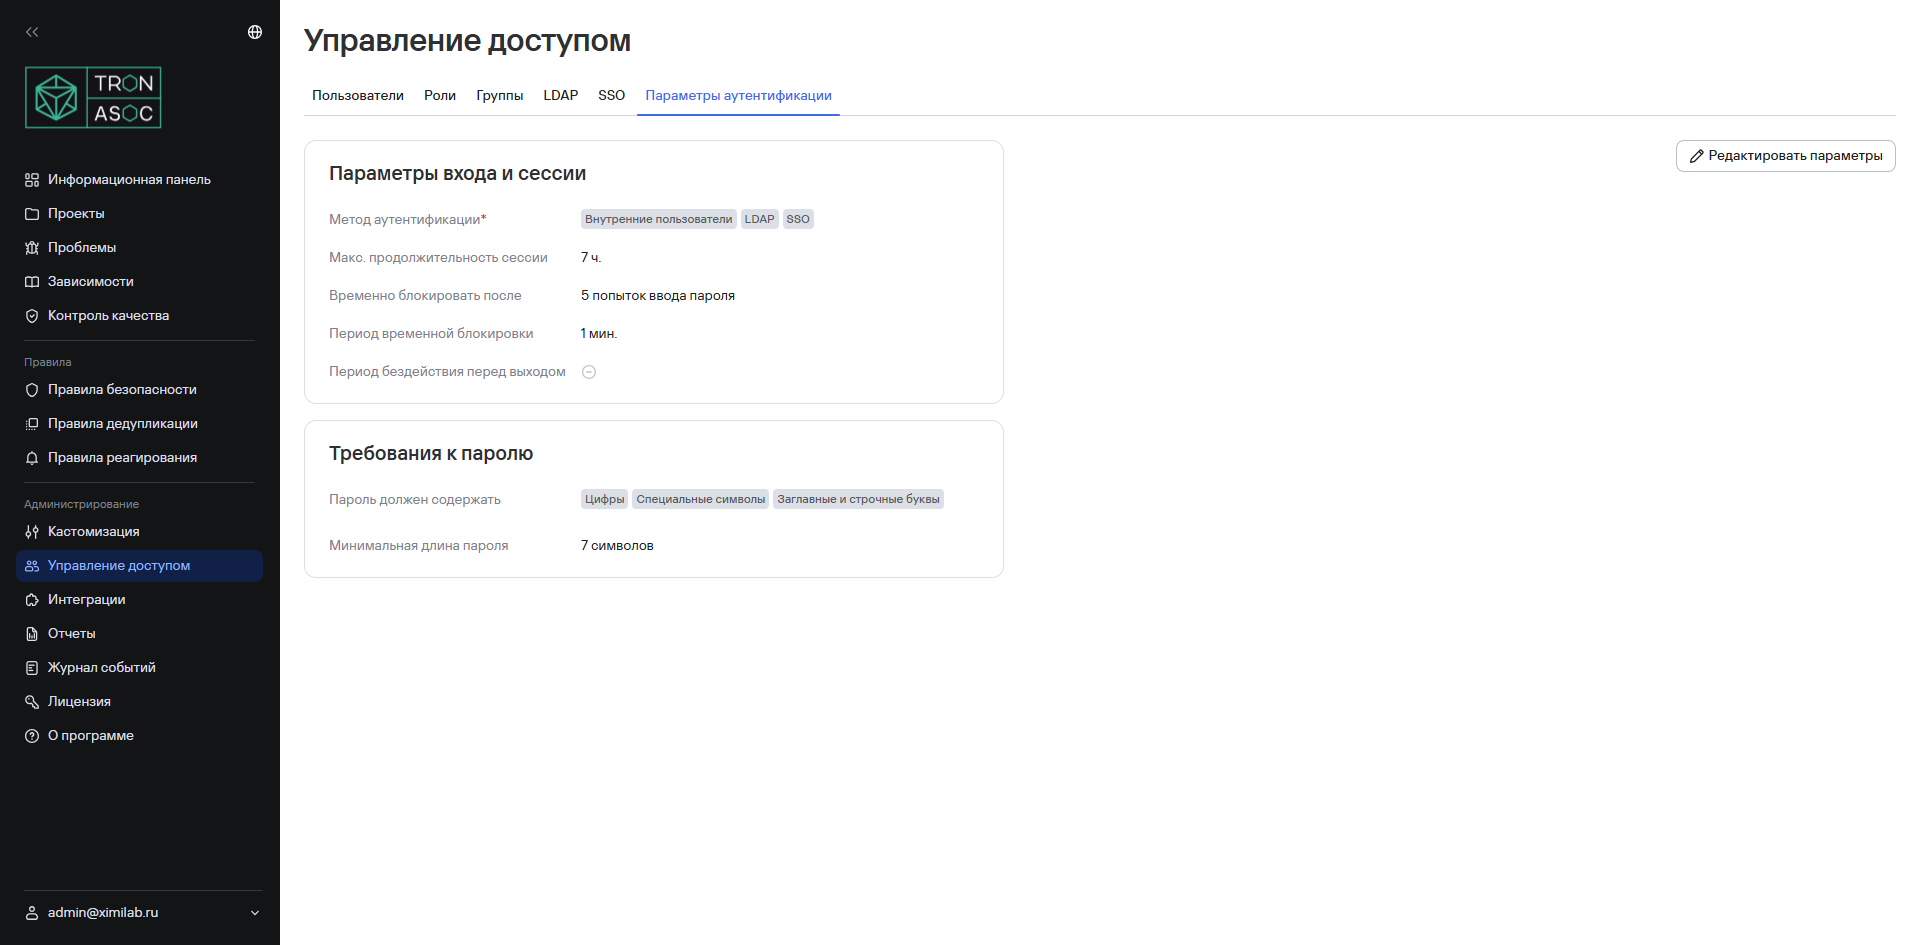
- configure authentication settings in TRON.ASOC.
The section contains the following subsections:
- Users;
- Roles;
- Groups;
- LDAP;
- SSO;
- Authentication settings.
Users
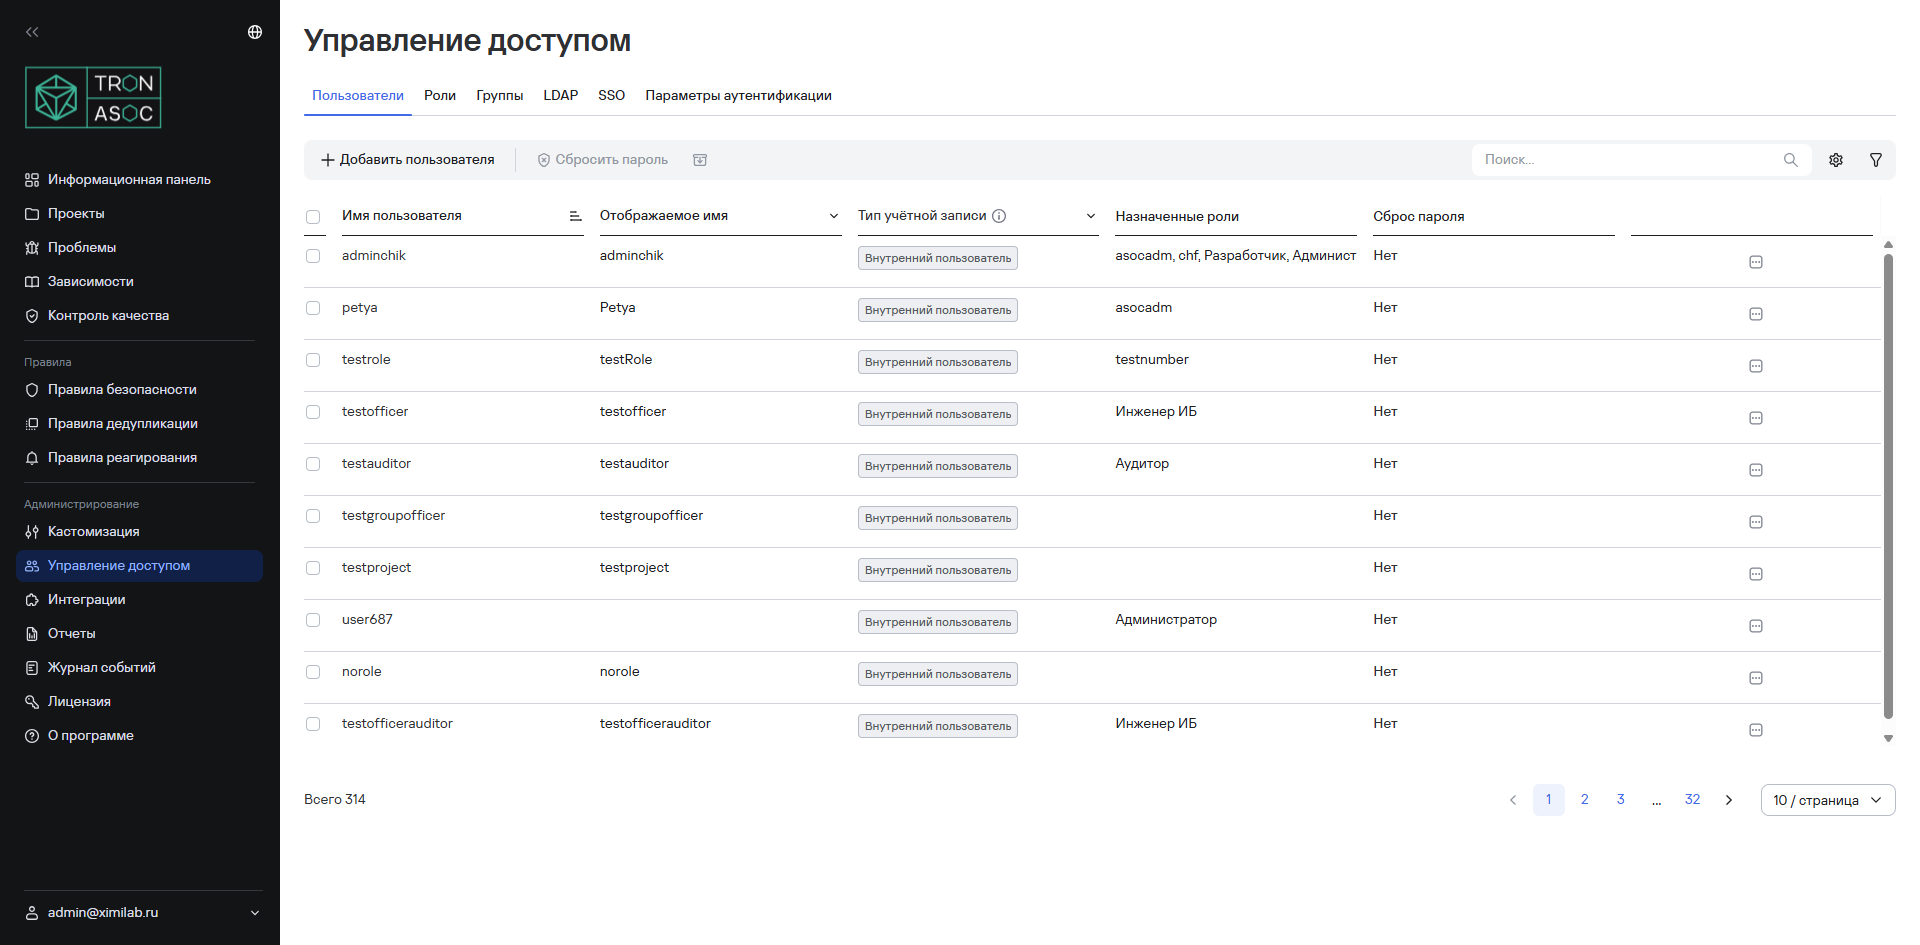
The Users subsection lists the following user information:
- Username—the user's unique login or identifier;
- Display name—the name that other users see;
- Assigned roles—the roles assigned to the user;
- Password reset—an indicator of whether the user needs to reset their password. A value of Yes means that the user must change their password the next time they sign in.
Roles
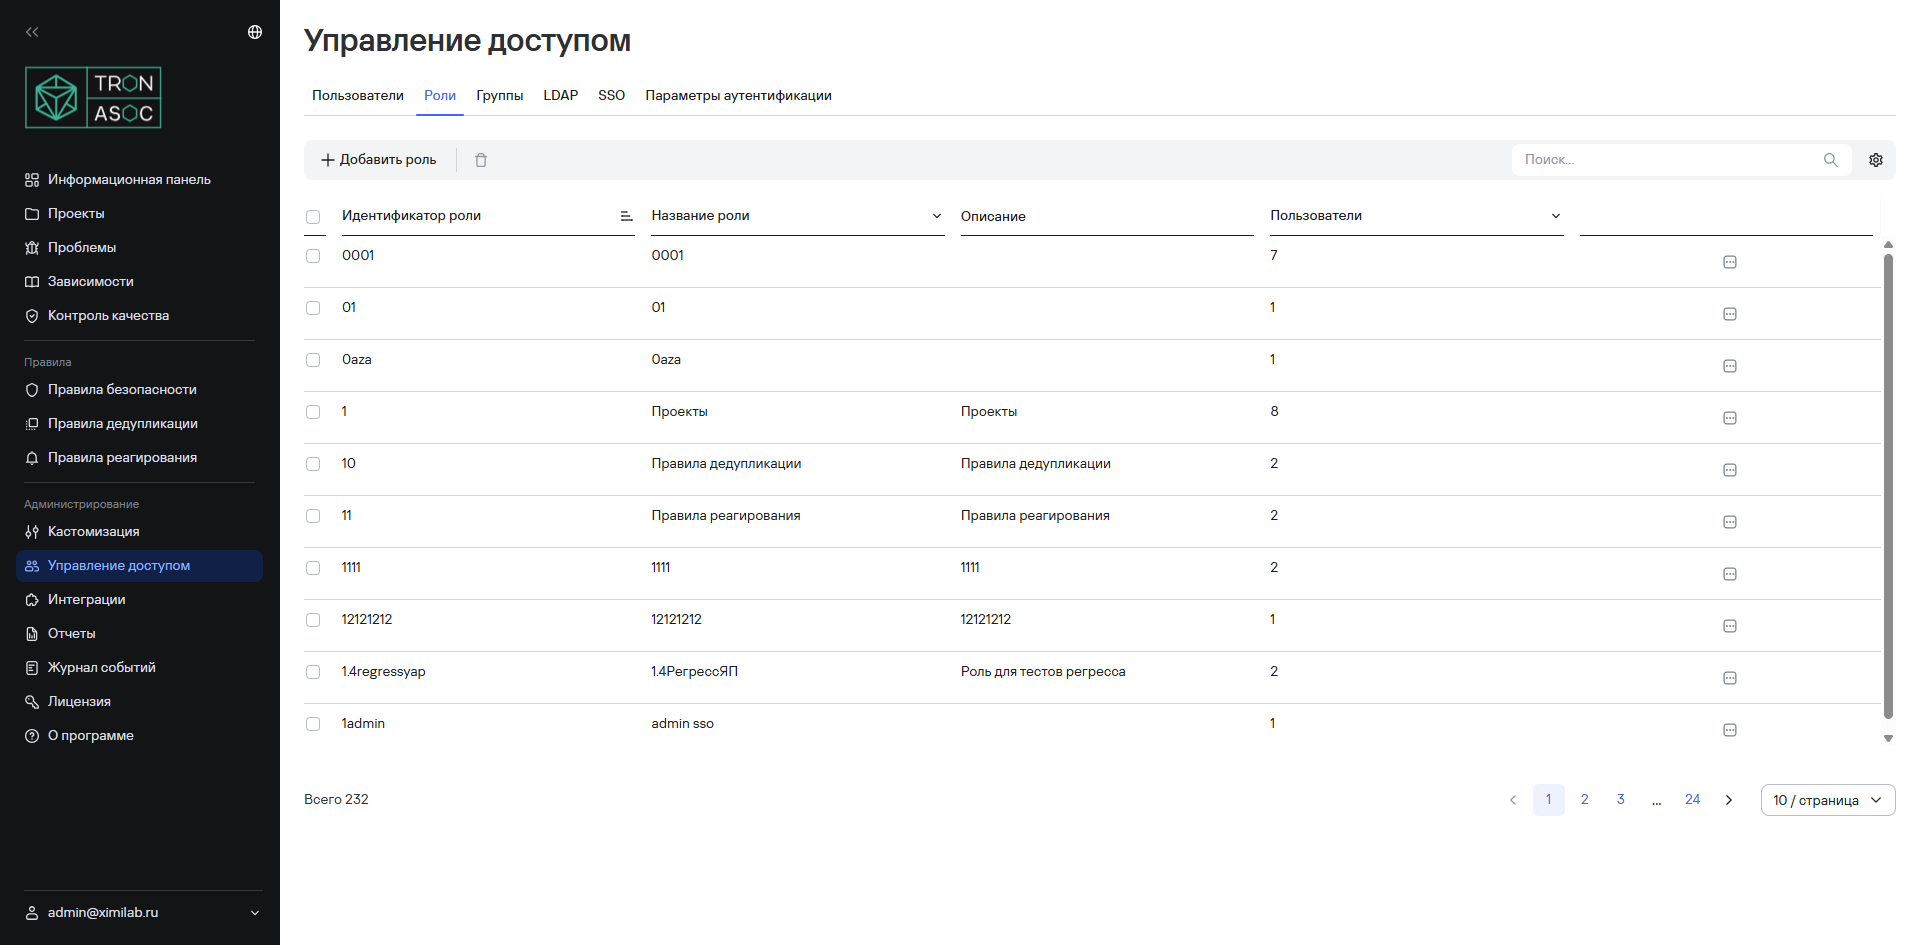
The Roles subsection displays all system roles and the number of users assigned to each role.
Base system roles
| Role | Description |
|---|---|
| Administrator (isadm) | A role with full permissions. The product assigns all existing permissions to this role during installation. It's intended for users responsible for deploying and maintaining the infrastructure and system software required to run the solution, for example, operating systems, application servers, and databases. These users are also responsible for creating and managing user accounts, roles, and access; changing settings; monitoring the license; and connecting security tools and scanning sources. |
| Auditor (isaud) | A role for monitoring data and system security, user actions, and system operations; analyzing event logs; and monitoring scan results and compliance with Quality Controls. |
| Information security engineer (isoff) | A role for monitoring and ensuring the information security of projects under development, configuring security rules, monitoring threats, and managing security tools and scans. |
| Developer (dev) | The minimum base role. It's intended for users who check compliance with standards, view scan results, and review excluded issues. |
- You can't delete the Administrator (isadm) role—you can only block it. In addition, TRON.ASOC requires at least one user with the Administrator (isadm) role.
- You can delete the other roles (Auditor (isaud), Information security engineer (isoff), and Developer (dev)).
Groups
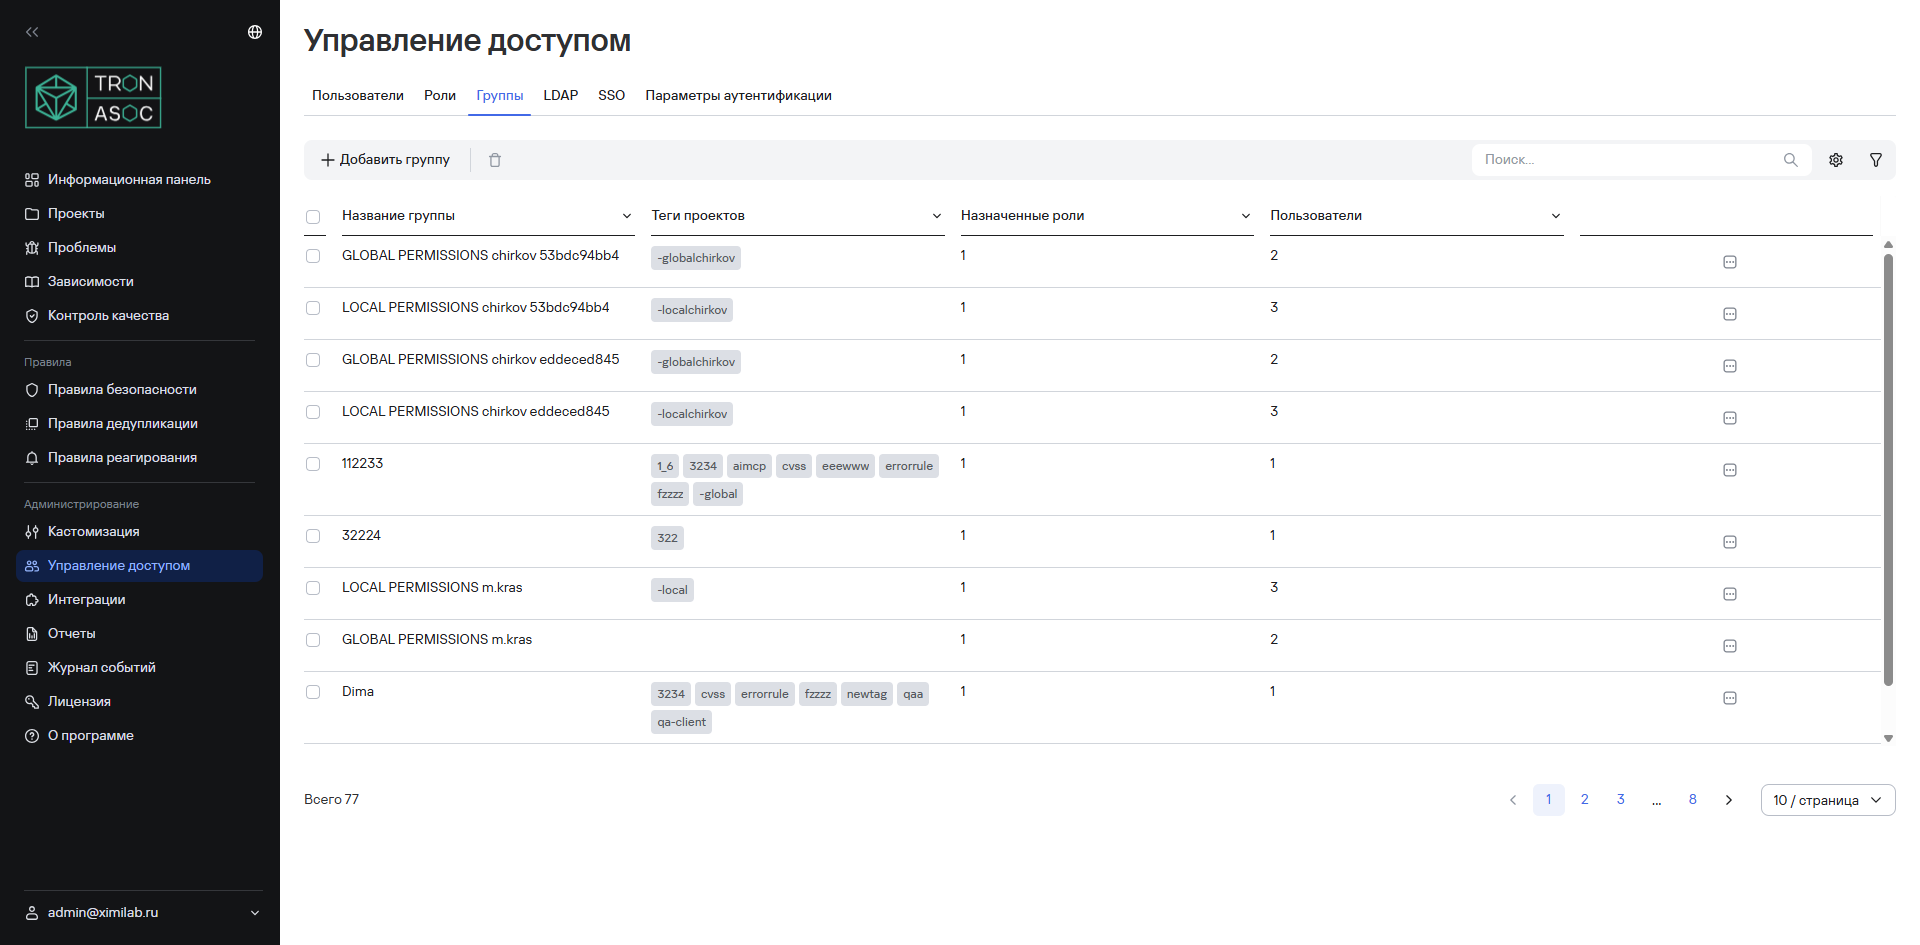
In the Groups subsection, you can create, edit, and delete user groups, add users to groups, and configure mapping with LDAP/SSO groups.
When you add users to a group, the group's additional permissions are added to the user's role permissions.
LDAP
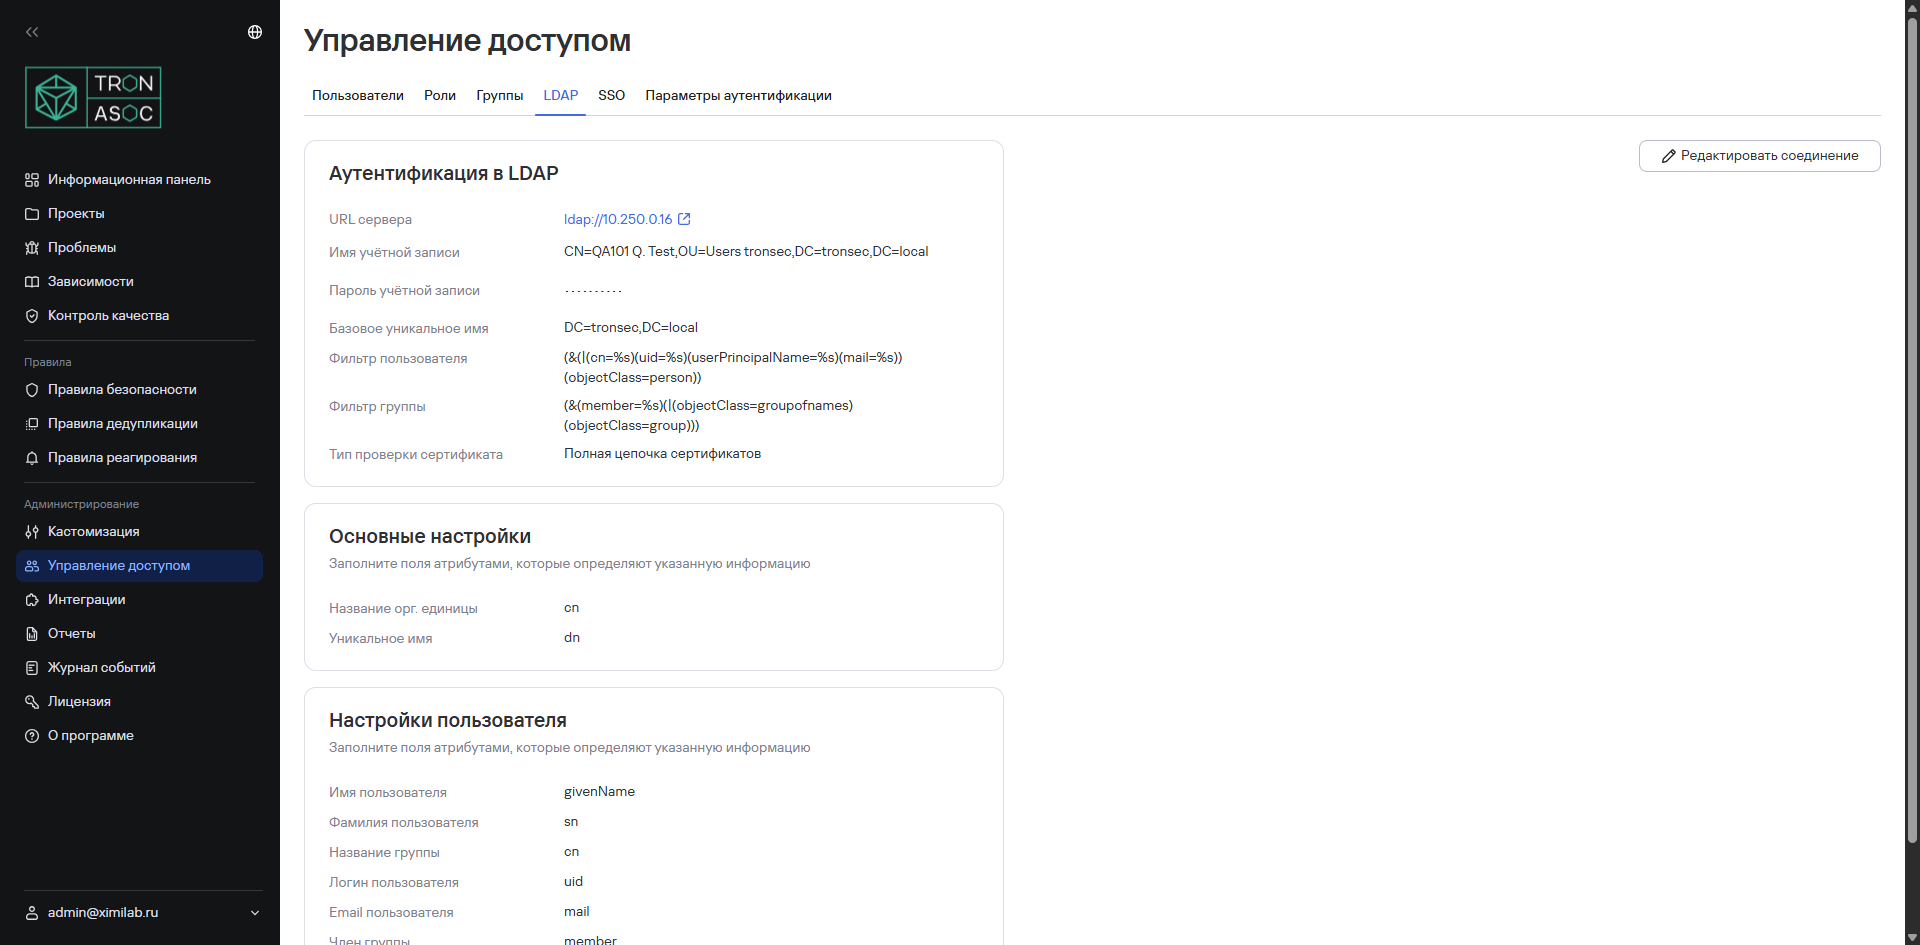
The LDAP subsection provides convenient and secure user and access management through integration with LDAP or AD.
SSO
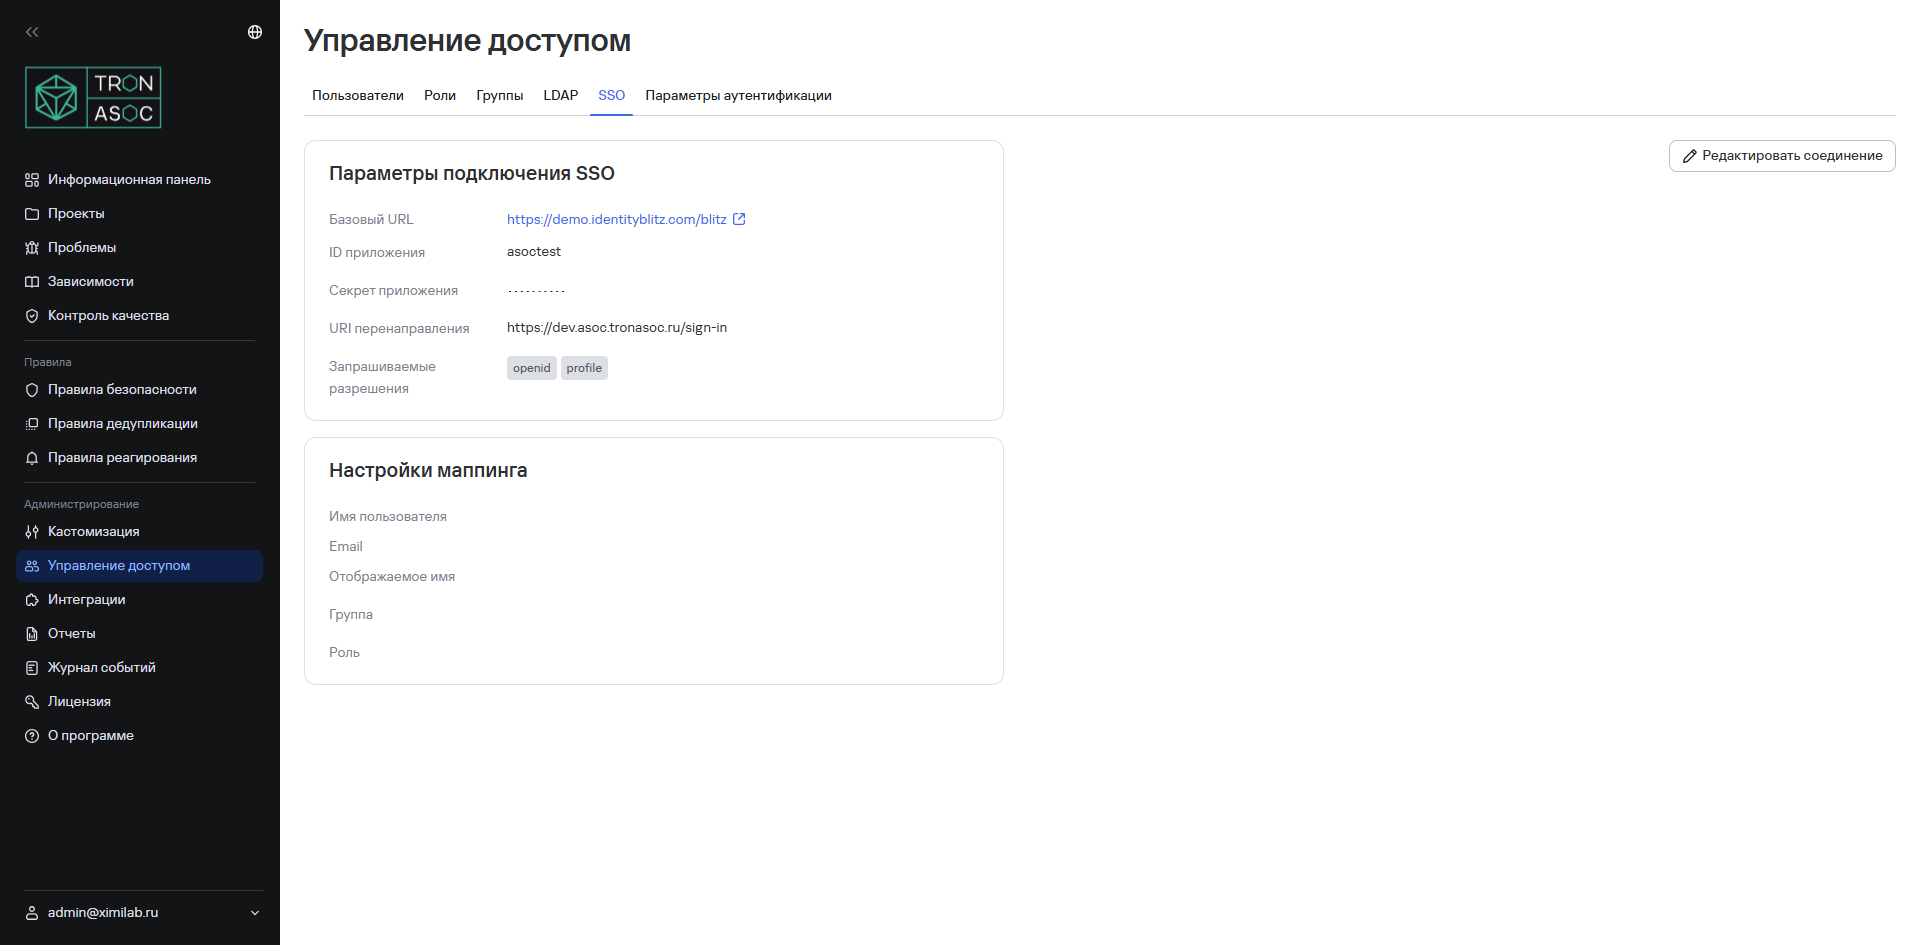
The SSO subsection lets you configure and manage users and their access through integration with IdP (Identity Provider) services, for example, Identity Blitz and Keycloak.
Authentication settings
In the Authentication settings subsection, you can configure the following parameters:
- authentication methods;
- maximum session duration;
- maximum number of incorrect password attempts before temporarily blocking the account;
- temporary account block duration;
- sign-out after inactivity;
- account Password requirements.