"Security rules" section
The system lets you create exclusion rules for handling results in the product. The Security rules section is designed to manage security rules that apply to vulnerabilities and other security issues in projects. This lets you temporarily or permanently ignore specific issue types based on their priority or other criteria.
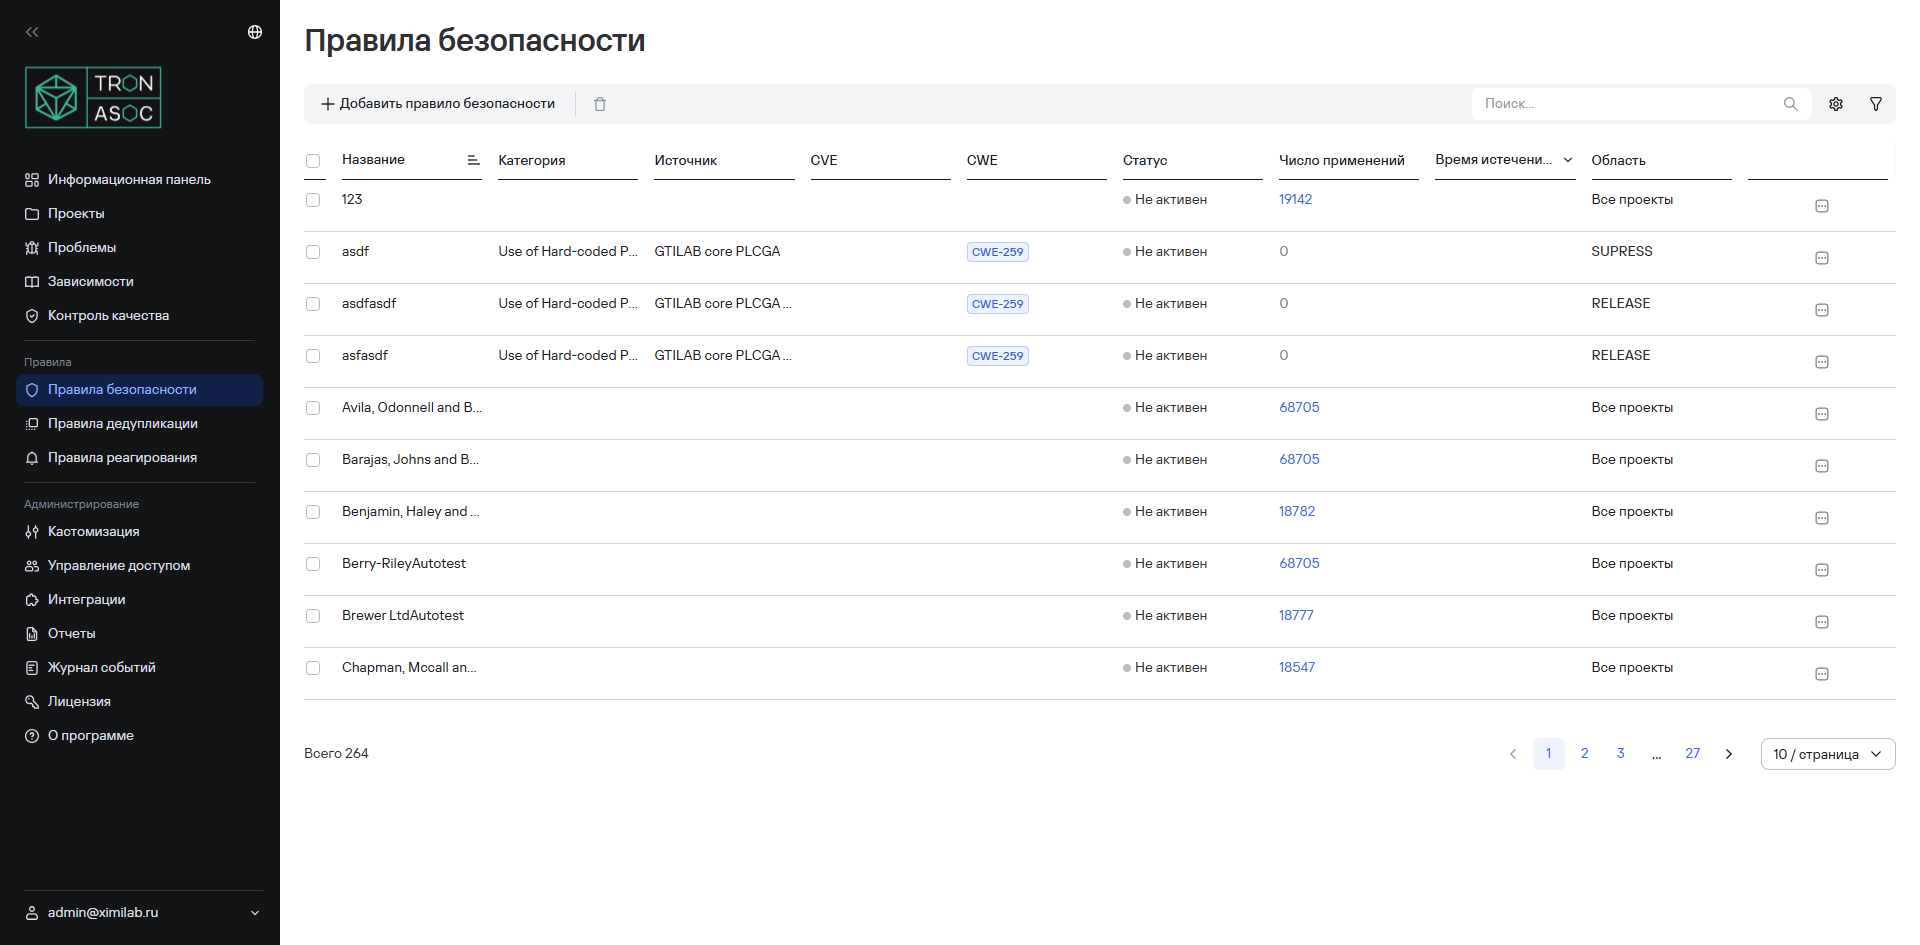
The section is designed to manage rules that apply to vulnerabilities and other security issues in projects.
Security rules apply to issues after scanning is complete (when launched from TRON.ASOC) and the scan results report is available. For more information, see Scan results.
Security rules table structure
Security rules appear in the Security rules section as a table. The table includes the columns listed below.
| Column | Description |
|---|---|
| Name | Security rule name or identifier |
| Category | Category of the issue to which the rule applies |
| Source | Scan source to which the rule applies |
| CVE | Unique vulnerability identifier in the CVE database |
| CWE | CWE code (Common Weakness Enumeration) |
| Status | Rule activity status |
| Number of uses | Number of times the rule has been applied |
| Expiration date | Date when the rule stops applying |
| Scope | Project scope |
Users can hide the columns they need, except for the Name column, and reorder the columns.
Filtering security rules
Users can configure which security rules appear by using the following filters:
- Created—the period when the security rule was created. Configure it with the From and To fields. Enter values in
DD.MM.YYYYformat. - Updated—the period when the security rule was updated. Configure it with the From and To fields. Enter values in
DD.MM.YYYYformat. - Expiration—the period when the security rule expires. Configure it with the From and To fields. Enter values in
DD.MM.YYYYformat. - Category
- Source
- CVE
- CWE
- Status