Security issues section
Security issues and information about them appear as a list in Projects → Project name → Issues or in Issues in the main menu.
The list of security issues includes the following parameters:
- Vulnerability ID—the ID of the detected security issue;
- False-Positive label—the indicator that the security issue is a false positive. It isn't a status and doesn't affect status changes;
- Duplicate label—the indicator that the security issue is a duplicate. It isn't a status;
- Covered by security policy label—the indicator that the issue falls under a security policy rule. It isn't a status;
- Category—the name of the security issue category;
- Severity—the severity of the security issue;
- Status—the status of the security issue;
- CVSS (v.2/v.3/v.4)—the security issue score according to the applicable CVSS standard;
- Exploitability—the detected exploitability;
- Tool—the name of the vulnerability detection tool;
- CWE—the CWE parameter name;
- CVE—the CVE parameter name;
- Source—the name of the scan source;
- Source branch/tag—the branch or tag of the scan source;
- File—the name of the scanned file;
- Line—the line number;
- Matching code—the source code contained in the security issue;
- Library—the library name;
- Project—the project name;
- Created—the date when the security issue was detected;
- Updated—the date when the security issue was updated;
- Last detected—the date when the security issue was last detected;
- AI FP analysis—the result of the AI false-positive analysis;
- Comments—comments and the number of unread comments;
- Assignee—users or user groups assigned as responsible parties.
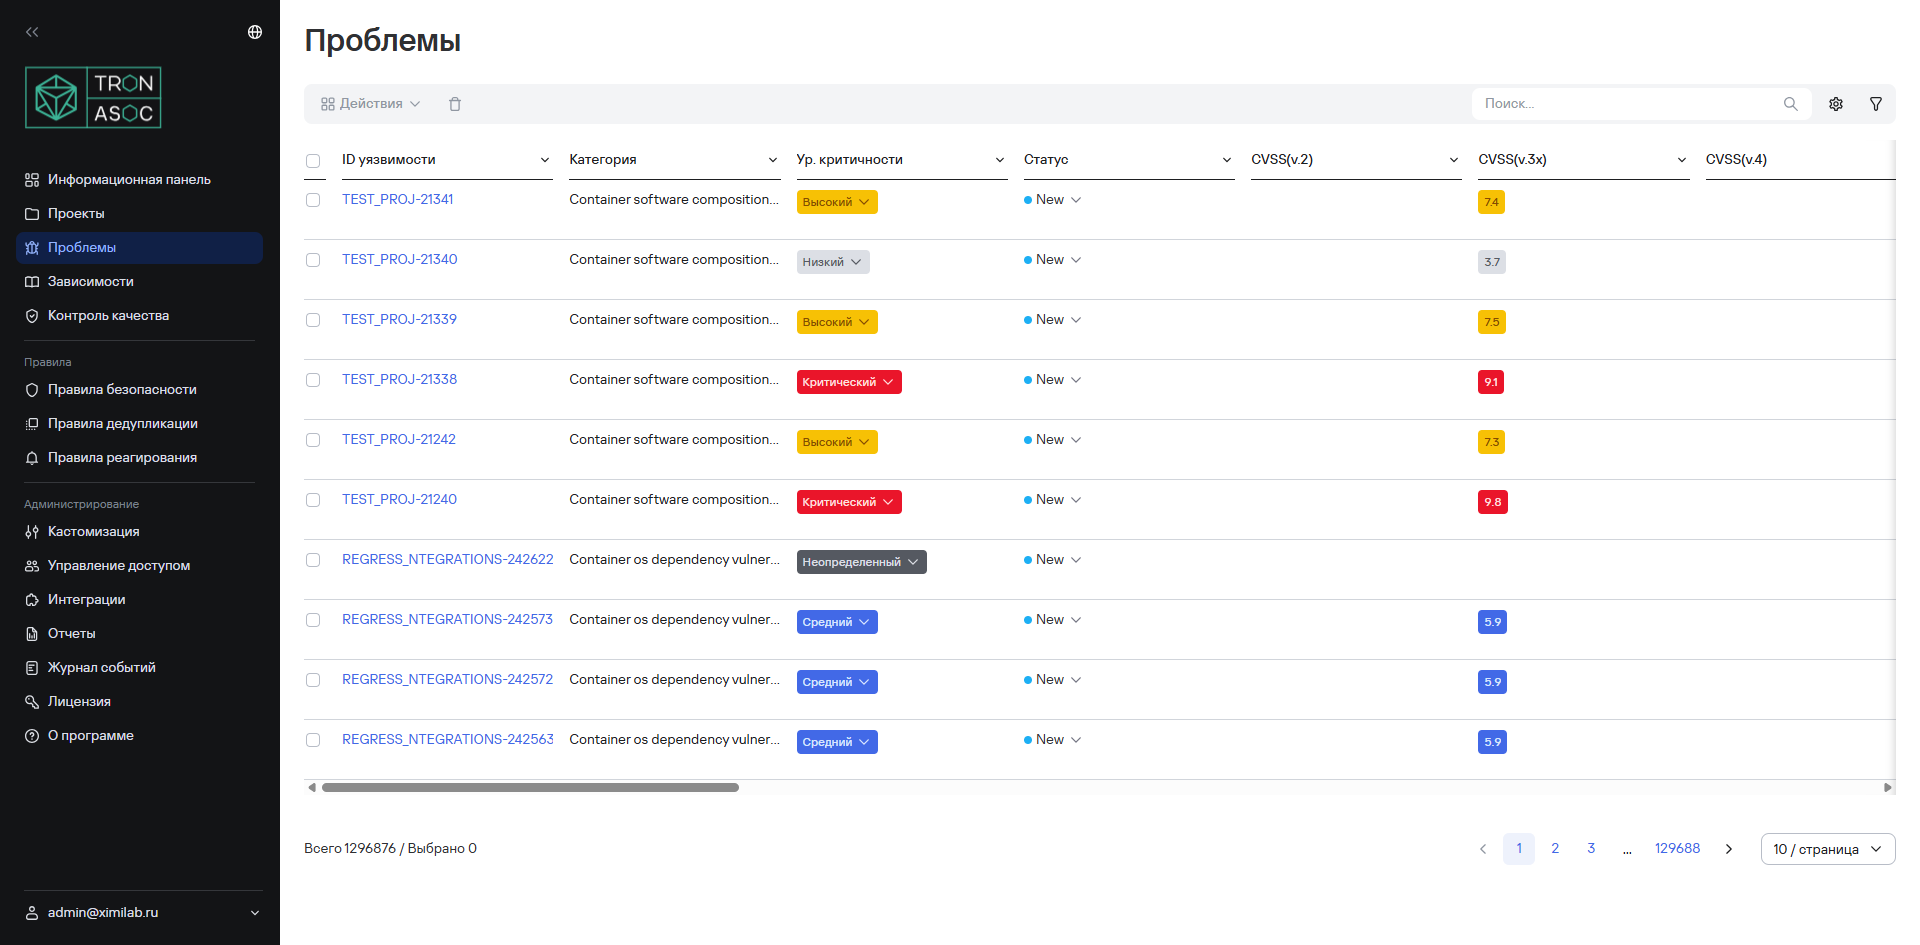
Users can perform the following actions on security issues:
- view detailed information about a security issue;
- change the visibility of security issue statuses;
- filter security issues by available attributes;
- search for security issues by CWE and CVE parameters;
- perform other bulk actions.