Dashboard
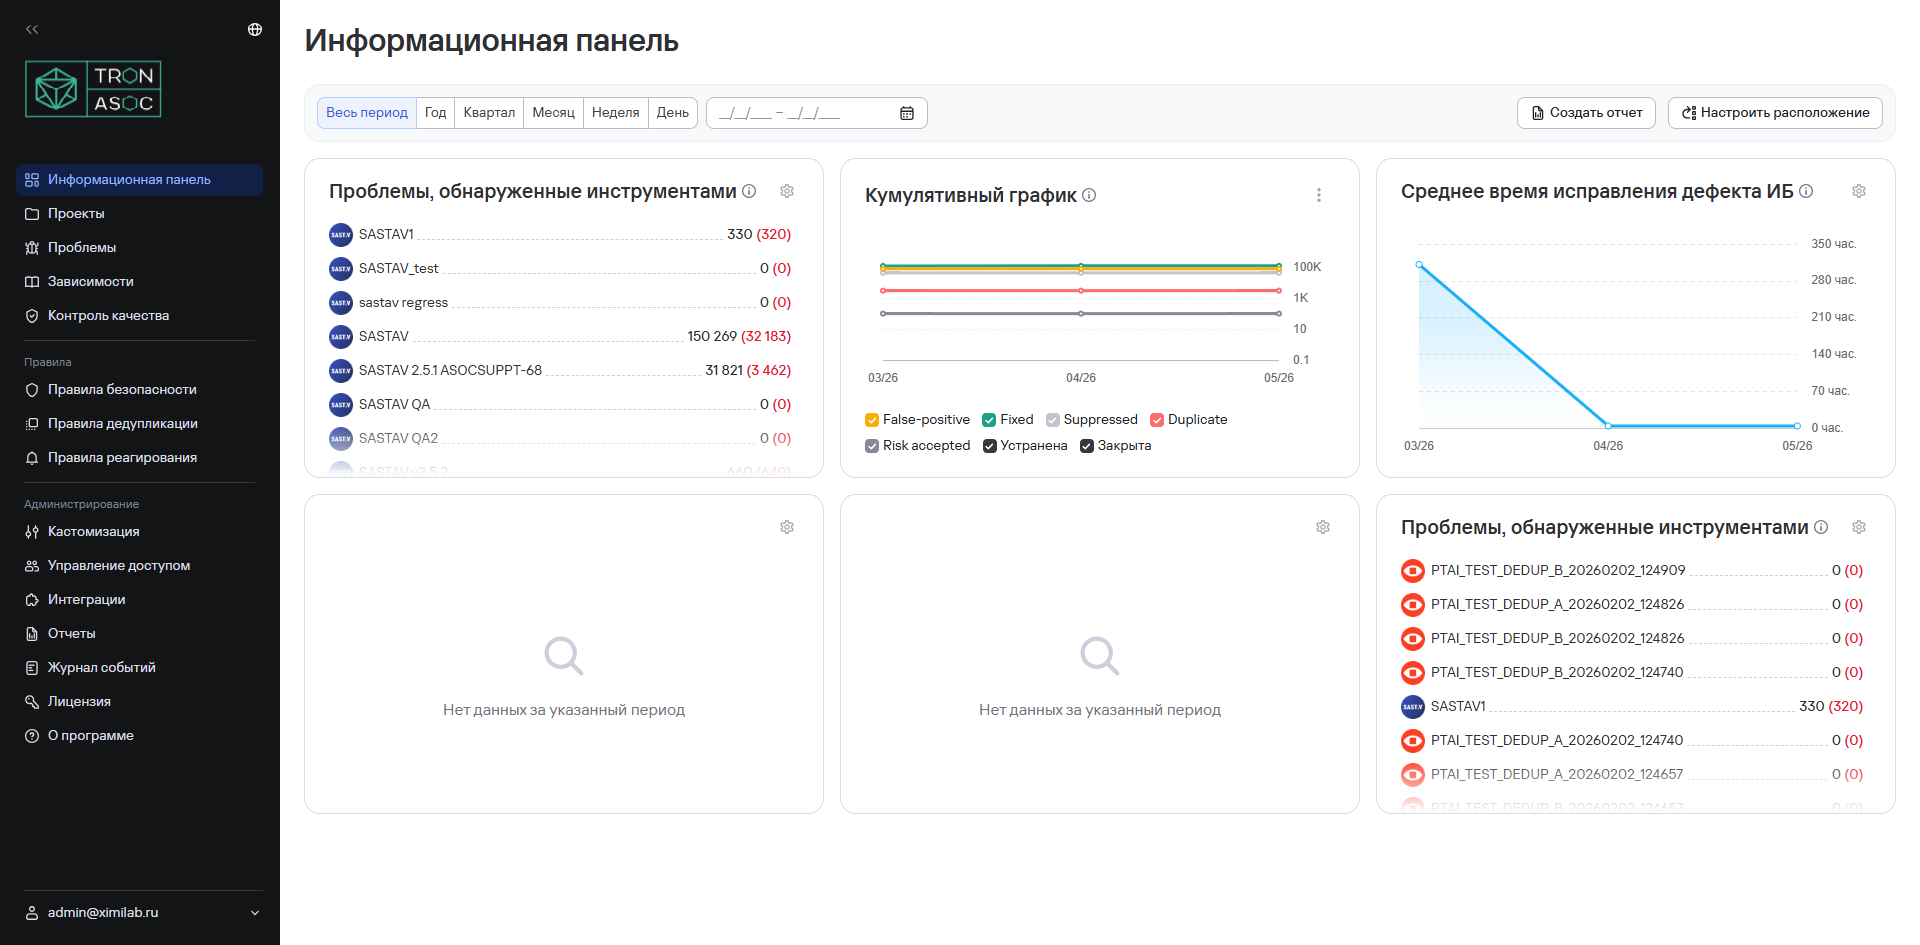
The dashboard contains summary graphs (widgets) for vulnerabilities during the selected period. Data updates once a day.
The dashboard includes the following widgets:
- Cumulative graph of detected vulnerabilities;
- Total number of open vulnerabilities;
- Most common open vulnerabilities;
- Most common critical and high vulnerabilities;
- Most vulnerable projects;
- Mean Time to Detect (MTTD);
- Security metrics;
- Scan Frequency Ratio;
- Number of vulnerabilities;
- Security Defect Lead Time;
- Fixed Vulnerabilities;
- Number of duplicate vulnerabilities;
- Number of false positives;
- Mean Time to Resolve;
- Risk Density;
- Integrated Risk Index.
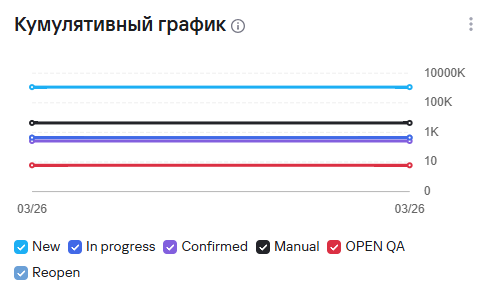
Cumulative graph of detected vulnerabilities
This widget shows vulnerability detection trends during the selected period. It also lets you analyze changes in the total number of security issues.
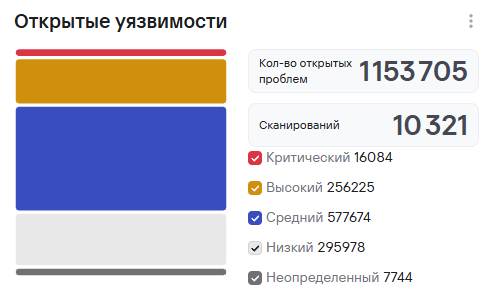
Total number of open vulnerabilities
This widget shows the total number of detected vulnerabilities, grouped by severity level and status.
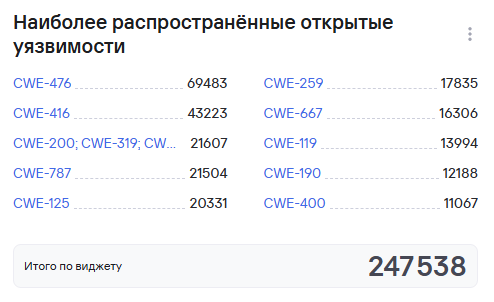
Most common open vulnerabilities
This widget shows the number of unresolved security issues that require processing or remediation.
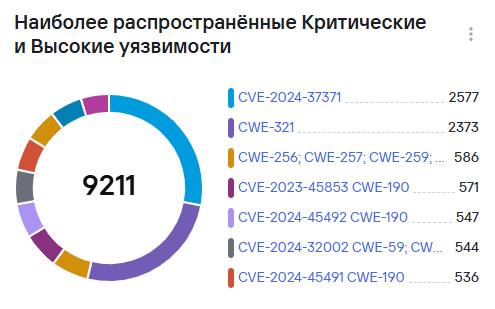
Most common critical and high vulnerabilities
This widget shows the most critical security issues with a high risk level and remediation priority.
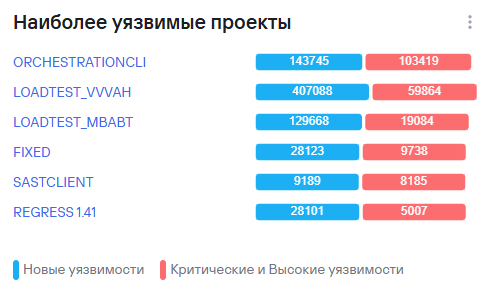
Most vulnerable projects
This widget shows projects with the highest number of detected security issues during the selected period.
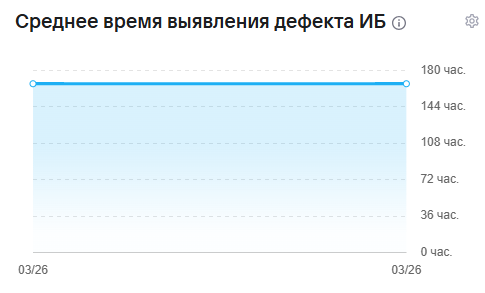
Mean Time to Detect (MTTD)
This widget shows the average time between the appearance of a security issue and its detection by analysis tools.
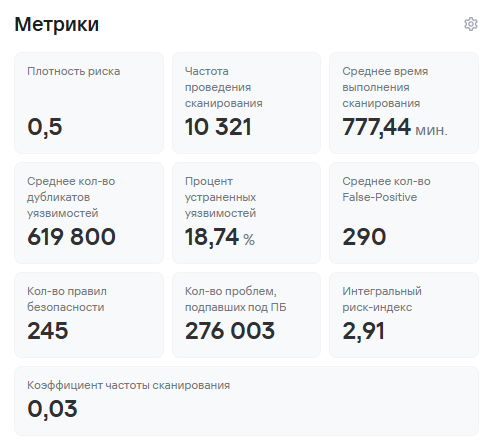
Security metrics
This widget shows key performance indicators for secure development processes and security issue handling.
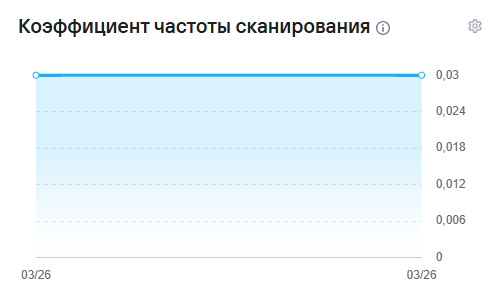
Scan Frequency Ratio
This widget shows the intensity of security checks and how often scans run in projects.
Number of vulnerabilities
This widget shows the total number of detected security issues during the selected period.

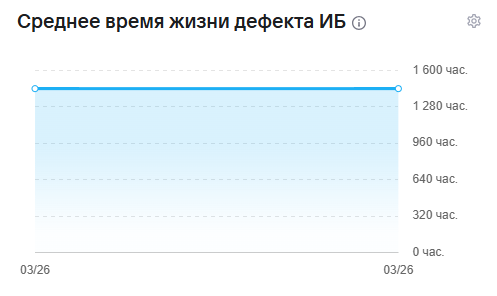
Security Defect Lead Time
This widget shows the median time a security issue exists, from detection to closure.
Fixed Vulnerabilities
This widget shows the ratio of closed security issues to the total number of detected vulnerabilities.

Number of duplicate vulnerabilities
This widget shows the number of security issues that the system identified as duplicates.

Number of false positives
This widget shows the number of false-positive vulnerabilities.

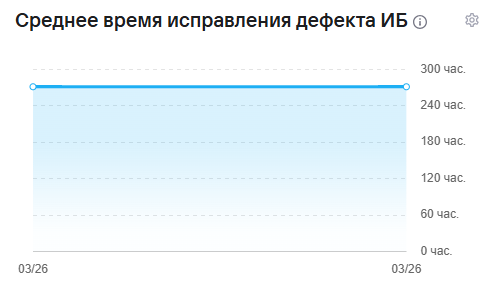
Mean Time to Resolve
This widget shows the average time spent remediating security issues.
Risk Density
This widget shows the concentration of security issues relative to the size of the analyzed application or project.

Integrated Risk Index
This widget shows a summary of the project's risk level based on the severity and number of detected vulnerabilities.

Metric calculation formulas
Secure development practice coverage
The secure development practice coverage metric uses the following formula:
Risk Density (M)
The Risk Density metric uses the following formula:
where:
- —the number of critical vulnerabilities in the project;
- —the number of high-severity vulnerabilities in the project;
- —the number of medium-severity vulnerabilities in the project;
- —the number of low-severity vulnerabilities in the project;
- —the number of vulnerabilities with an undefined severity level in the project;
- , , , , —the weighting factors for each severity level;
Note: , , , ,
- —the total number of vulnerabilities in the project.
The metric uses the following formula:
Integrated Risk Index
The Integrated Risk Index metric uses the following formula:
where:
- —Risk Density;
- —Scan Frequency Ratio;
- —the remediation time factor.
V factor
The V factor (scan frequency) uses the following formula:
where:
- —the scan frequency for the project.
- —the minimum scan frequency among all projects.
- —the maximum scan frequency among all projects.
The formula normalizes the project's scan frequency against the minimum and maximum values across all projects. The factor ranges from 0 to 1:
- A value close to 0 indicates a low scan frequency.
- A value close to 1 indicates a high scan frequency.
Defect remediation and identification time factor L
This factor measures the speed of vulnerability remediation against the median value. It uses the following formula:
where:
- —the current Mean Time to Resolve a vulnerability.
- —the current Mean Time to Detect a vulnerability.
- —the median time to resolve vulnerabilities across all projects.
- —the median time to detect vulnerabilities across all projects.
The factor shows how defect handling time differs from median values:
- A value of means that the project fixes and detects vulnerabilities faster than the median.
- A value of corresponds to the median level.
- A value of means that the project handles vulnerabilities more slowly than the median.
Other metrics
Fixed Vulnerabilities
This metric is calculated as the ratio of closed vulnerabilities to the total number of vulnerabilities in the project.
Average time in a specific status
This metric is calculated as the median time spent in each status, expressed as a whole number of hours.
Security Defect Lead Time
The Security Defect Lead Time is calculated as the median defect lifetime—from the New status to any closed status, for example, Fixed.
Mean Time to Detect (MTTD)
This metric is calculated as the median time to identify defects in one or more projects. Defect identification means changing the status from New to any subsequent status.
Mean Time to Resolve (MTTR)
This metric is calculated as the median time from an open status other than New to a closed status.